
How do I prepare Cyber Essentials Certification?
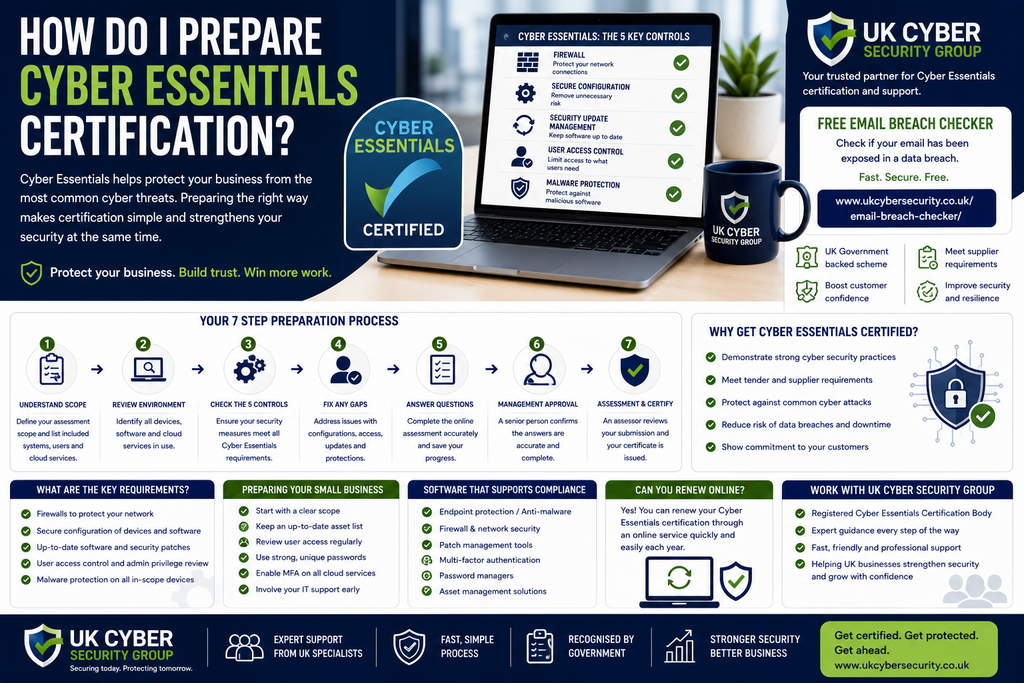
How do I prepare Cyber Essentials Certification?
Preparing for Cyber Essentials Certification becomes much easier when you treat it as a practical review of your everyday IT security rather than an exercise in answering assessment questions.
Cyber Essentials is the UK Government-backed cyber security scheme designed to help organisations protect themselves against many common internet-based attacks. It concentrates on five core technical controls: firewalls, secure configuration, security update management, user access control and malware protection.
As of August 2026, organisations opening a new Cyber Essentials assessment use the Cyber Essentials Requirements for IT Infrastructure v3.3, which became effective on 27 April 2026. The National Cyber Security Centre confirms that applications created before that date can continue using the previous requirements that applied when the assessment started.
The best preparation starts before you submit anything. You should understand your assessment scope, know which devices and cloud services your business uses, identify unsupported software, review administrator access, check multi-factor authentication and make sure your five Cyber Essentials controls work in practice.
UK Cyber Security Group provides Cyber Essentials certification and confirms that it operates as a registered Cyber Essentials Certification Body. It can guide organisations through the application process and provide additional support where required.
Cyber Essentials preparation starts with knowing your environment
Many failed assessments begin with incomplete information.
A company may know that its staff use Windows laptops but not know which operating system versions they run. It may use Microsoft 365 but overlook another cloud service used by the sales team. Employees may have administrator privileges that nobody has reviewed for years.
You need a reasonably accurate picture of your IT environment before answering the assessment questions.
Start by identifying:
Desktop computers
Laptops
Mobile devices used for business
Servers
Routers and firewalls
Operating systems
Business applications
Cloud services
Remote working arrangements
User accounts
Administrator accounts
This exercise does not need to become complicated.
The purpose is to make sure the answers you submit reflect your real business environment.
Download the current assessment questions first
One of the easiest ways to prepare involves reviewing the Cyber Essentials questions before starting your formal assessment.
The NCSC provides the current assessment questions and technical requirements through its Cyber Essentials resources.
IASME also encourages organisations to prepare before completing the online assessment.
Use the questions as an internal security review.
Read each one and ask:
Do we understand what this question asks?
Who in the business knows the answer?
Can we verify the answer?
Does our current setup meet the requirement?
Do we need to make a change before submitting?
This approach reduces surprises.
It also gives your IT provider or internal technical staff enough time to correct weaknesses before an assessor reviews the application.
Understand the current 2026 requirements
Cyber Essentials requirements receive regular updates so the scheme continues to reflect changing technology and cyber threats.
The current Requirements for IT Infrastructure v3.3 applies to assessment accounts created from 27 April 2026 onwards. IASME stated that the 2026 changes mainly improve clarity and consistency while also strengthening certain assessment requirements.
One particularly important area involves multi-factor authentication.
IASME confirms that MFA is mandatory for cloud services where the service makes it available. Under the current marking criteria, failing to enable available MFA for an applicable cloud service results in assessment failure.
Do not leave this check until the end of your preparation.
Review your cloud environment early.
What are the key requirements for achieving Cyber Essentials certification?
Cyber Essentials centres on five technical controls.
Each one addresses a common route that attackers can use to compromise organisations.
Firewalls
Firewalls help control communication between your organisation’s devices or networks and the internet.
You need to understand what protects your internet connections and how you manage access.
Review whether unnecessary inbound connections exist.
Check who can change firewall settings.
Make sure any administrative interfaces receive suitable protection.
For many smaller businesses, security functions built into routers, operating systems and cloud environments may form part of the solution.
The important issue is whether those controls operate correctly.
Secure configuration
Devices and services often arrive with functionality that an organisation does not need.
Every unnecessary account, service or feature can create additional exposure.
Secure configuration involves reducing that exposure.
Review default accounts.
Remove or disable unnecessary software.
Check whether devices use sensible security settings.
Remove unused accounts.
Review browser and application configurations where relevant.
The objective is not to make technology difficult to use.
It is to remove unnecessary opportunities for an attacker.
Security update management
Attackers regularly exploit known software vulnerabilities.
Cyber Essentials therefore requires organisations to use supported software within the assessment scope and manage security updates appropriately.
Review:
Operating systems
Browsers
Office applications
Server software
Mobile operating systems
Business applications
Router and firewall firmware where relevant
Cloud applications under your control
Do not assume software remains supported simply because it still works.
Check the supplier’s current support information.
Unsupported software inside the assessment scope can prevent certification.
This makes software support one of the first areas you should investigate when preparing.
User access control
Employees should receive the access they need to perform their work, but no more than necessary.
Review every important user account.
Ask:
Does this person still work here?
Does the employee still need this account?
Does the person need access to this information?
Does the user genuinely require administrator privileges?
Have any shared accounts become unnecessary?
Administrator access deserves particular attention.
Users should not routinely carry out ordinary work through administrator accounts when elevated access is unnecessary.
Separate administration from normal activity where appropriate.
Malware protection
Cyber Essentials requires organisations to protect devices against malicious software.
Depending on your environment, appropriate protection may involve anti-malware functionality, application controls or another permitted approach under the scheme requirements.
Review whether protection remains active.
Check whether devices receive current security information.
Make sure employees cannot casually disable protection.
You should also know which devices fall within the assessment because overlooked computers can create gaps.
Define the assessment scope accurately
Scope tells the Certification Body what your certificate covers.
This is one of the most important preparation tasks.
Think about:
Which legal organisation seeks certification?
Which employees use company IT?
Which locations apply?
Which devices connect to business services?
Which cloud services support the business?
How do remote workers operate?
Which networks connect with organisational information?
A narrow or inaccurate scope can create problems.
Do not assume that cloud services disappear from consideration simply because another company hosts them.
Modern Cyber Essentials assessments place significant emphasis on cloud services because businesses increasingly depend on platforms such as Microsoft 365, Google Workspace and other hosted business applications.
Your Certification Body can help you clarify scope before you submit the assessment.
Create a reliable asset list
You cannot secure equipment that nobody knows exists.
Create an inventory of relevant devices.
You might record:
Asset identifier
Device purpose
Operating system
Operating system version
Primary user
Business location
Support status
You do not need to turn a small organisation’s asset list into an enormous database.
Accuracy matters more than complexity.
A useful inventory helps you answer assessment questions, identify unsupported technology and maintain Cyber Essentials after certification.
Cloud services also need attention.
Keep a record of the business platforms employees use.
Shadow IT can cause problems when teams start using online services without informing IT or management.
Check every operating system for support
Software support represents a major Cyber Essentials issue.
Review every operating system within scope.
Common examples include:
Microsoft Windows
Apple macOS
Apple iOS
Android
Linux distributions
Server operating systems
Check the version, not only the product name.
A supported operating system can still contain an older release that no longer receives security fixes.
The same principle applies to applications.
If the supplier no longer provides security updates, you need to address that position before relying on the software within the assessment scope.
Review internet-facing services
Internet exposure deserves careful attention.
Identify services that people can reach directly from the internet.
These could include:
Remote access services
Web applications
VPN services
Administrative interfaces
Email systems
Cloud portals
Server services
Ask whether each exposed service genuinely needs to remain available externally.
If it does, ensure that authentication and security controls meet the relevant requirements.
If it does not, remove the unnecessary exposure.
Reducing unnecessary internet-facing services removes opportunities for attackers.
Review your cloud services
Cloud security now plays a major role in Cyber Essentials.
Create a list of services employees use for organisational work.
Examples might include:
File sharing
Accounting
Customer relationship management
Project management
Collaboration
Human resources
Support platforms
Development platforms
For each service, identify who manages it and which users have access.
Then check multi-factor authentication.
IASME’s current 2026 guidance makes clear that organisations need to enable MFA for cloud services where it is available.
Do not assume that employees have enabled it simply because the service supports it.
Verify the configuration.
Make multi-factor authentication a priority
MFA provides one of the strongest practical improvements you can make before Cyber Essentials assessment.
Start with cloud services.
Review normal users and administrator accounts.
Check whether the service has MFA available.
Confirm that users actually enrolled.
Look for exceptions.
Review any legacy authentication that might bypass stronger security.
Administrator accounts deserve particular attention because compromise can give an attacker significant control.
If your organisation has delayed MFA because employees find it inconvenient, Cyber Essentials preparation provides a strong reason to complete the work.
Review administrator privileges
Administrator accounts give users powerful capabilities.
They can change settings, add software, alter security controls and manage other users.
That power creates risk.
Identify everyone who holds administrator access.
Ask why they need it.
Remove unnecessary privilege.
Where practical, give technical employees separate accounts for administration and everyday work.
Also review local administrator rights on employee computers.
A user may have received local administrator access years ago for one task and kept it ever since.
Cyber Essentials preparation provides an opportunity to correct that problem.
Remove old and unused accounts
Old accounts create avoidable attack opportunities.
Review:
Former employees
Contractors
Temporary workers
Test accounts
Service accounts
Shared accounts
Old administrator accounts
Cloud application accounts
Disable or remove access that no longer has a legitimate purpose.
Your employee leaver process should trigger this activity automatically in future.
Do not rely on an annual Cyber Essentials assessment to discover former employees who still have access.
Review password controls
Strong account security needs more than asking employees to invent complicated passwords.
Make sure password controls follow current Cyber Essentials requirements.
Avoid password reuse.
Use secure account recovery.
Consider password managers where appropriate.
Protect important accounts with MFA.
Make sure default credentials have been changed.
Check whether administrator accounts receive stronger protection.
Employees should also know how to report an unexpected authentication request.
A surprise MFA notification can indicate that somebody already knows the user’s password.
How can I prepare my small business for Cyber Essentials assessment?
A smaller business can prepare effectively without creating unnecessary administration.
Use a simple sequence.
First, download the current questions.
Second, define your scope.
Third, list devices and cloud services.
Fourth, check software support.
Fifth, review user and administrator accounts.
Sixth, verify MFA.
Seventh, review security updates.
Eighth, confirm firewall arrangements.
Ninth, check malware protection.
Tenth, correct any gaps before submitting the assessment.
IASME states that applicants can use the online assessment platform to answer the questions and save progress before submission. A senior person within the organisation must confirm that the submitted answers are accurate.
Preparation should involve whoever actually manages your IT.
That might be an employee, managed IT provider or cyber security company.
Do not guess technical answers.
Ask the person who can verify the configuration.
Use the Cyber Essentials Readiness resources
IASME and the NCSC provide preparation material specifically to help organisations understand the scheme.
These resources can help you identify gaps before formal assessment.
Use them to educate managers as well as technical staff.
Cyber Essentials works best when the organisation understands why the controls matter.
Preparation should improve security, not merely generate acceptable questionnaire responses.
If the readiness process uncovers unsupported software, excessive administrator access or missing MFA, correct the underlying issue.
Do not try to solve a technical weakness with creative wording.
Give yourself enough time
Once you apply, the Cyber Essentials process has a defined completion period.
IASME’s current terms state that applicants must complete and submit the assessment within six months. The certificate, once issued, remains valid for 12 months.
Six months may sound generous, but avoid using it as a reason to delay preparation.
Some issues take time to resolve.
Replacing unsupported equipment may involve planning.
Changing cloud authentication may require employee communication.
Removing administrator access can uncover applications that rely on unnecessary privilege.
Supplier-managed systems may need external support.
Resolve these matters before your formal deadline becomes a concern.
Understand what happens after submission
A qualified assessor working through a Certification Body reviews your Cyber Essentials answers.
IASME’s current guidance states that an assessor normally reviews submissions within three working days. If clarification or further information is necessary, the applicant can update its response and resubmit.
Assessment therefore involves human review.
The portal does not simply award a certificate because every box contains an answer.
The assessor checks whether the responses demonstrate compliance with the scheme requirements.
Clear, accurate answers make this easier.
Provide enough information for the assessor to understand your environment without adding irrelevant material.
Prepare supporting information before submission
Some answers may require information from your IT provider or system administrators.
Collect it before you submit.
Useful preparation records can include:
Device inventory
Operating system information
Cloud service list
MFA status
Administrator account list
Firewall information
Software support records
Security update information
Malware protection status
You do not necessarily need to submit every internal record.
Having the information available helps you answer accurately and respond quickly when the assessor asks for clarification.
What happens if the first assessment does not pass?
A failed first assessment does not always mean the entire process ends immediately.
IASME’s current Cyber Essentials terms allow one further assessment without another charge when the applicant resubmits within 48 hours of receiving notification that the initial submission failed.
This window suits straightforward corrections.
It does not provide much time for major technical projects.
That is another reason preparation matters.
Do not depend on the resubmission window to replace unsupported systems, restructure a complicated network or deploy MFA across a poorly documented environment.
Resolve significant issues before submission.
What software solutions support compliance with Cyber Essentials standards?
No single software product guarantees Cyber Essentials certification.
Technology can support the controls, but your organisation still needs to configure and operate it correctly.
Useful solutions can include endpoint management platforms that provide visibility of devices and security updates.
Identity platforms can help you manage user accounts, administrator privileges and MFA.
Endpoint security products can support malware protection.
Asset management platforms can help identify devices and applications.
Cloud administration consoles can help verify authentication and user configuration.
Password managers can support unique credentials.
Vulnerability management tools can help technical teams identify security weaknesses.
The correct combination depends on your environment.
A ten-person consultancy using cloud services may need a very different toolset from a company running servers, remote networks and specialised applications.
Focus on the requirements rather than collecting products.
Do not rely on software alone
Cyber Essentials involves technology, but people still need to manage that technology.
A security update platform provides little benefit if nobody reviews failed deployments.
MFA helps only when relevant users actually enable it.
An asset management system cannot protect a laptop that nobody added to the system.
A firewall does not reduce risk when administrators leave unnecessary access rules permanently enabled.
Make ownership clear.
Someone should know who manages each important control.
Prepare remote workers properly
Home and remote working arrangements can affect Cyber Essentials scope and security.
Understand which devices remote employees use.
Determine how they access organisational services.
Review whether employees use company-owned or personally owned equipment.
Check authentication.
Consider how devices receive security updates and malware protection.
Make sure remote working does not create unmanaged equipment that nobody considered during assessment preparation.
The same principle applies to employees who regularly work from client sites or shared working environments.
Talk to your IT provider early
Many smaller organisations outsource most IT management.
That can work well for Cyber Essentials, but you still remain responsible for answering the assessment accurately.
Speak with your provider before applying.
Ask them to help confirm:
Asset information
Operating system support
Security update arrangements
Firewall configuration
MFA status
Administrator accounts
Malware protection
Cloud services
Do not assume your managed service automatically means you comply.
Ask direct questions and verify the answers.
Explain Cyber Essentials to senior management
A senior person in the organisation must confirm that the submitted information is accurate. IASME’s current assessment guidance specifically includes senior confirmation before submission.
That person should understand what they approve.
Give management a short briefing.
Explain:
What the assessment covers
Which weaknesses you found
What actions you completed
Whether any significant concerns remain
Which business services fall within scope
This creates stronger accountability and helps security receive appropriate management attention.
Cyber Essentials reflects real UK cyber risk
The latest UK Government Cyber Security Breaches Survey shows why basic cyber security controls remain important.
The 2025 to 2026 survey found that 43 per cent of UK businesses identified a cyber breach or attack during the previous 12 months. That equates to approximately 612,000 businesses.
Reported incidence increased with organisational scale. The survey found that 65 per cent of medium businesses and 69 per cent of large businesses identified a breach or attack. Small businesses reported 46 per cent.
Phishing remained the most common attack method, affecting 38 per cent of UK businesses.
These figures do not mean Cyber Essentials can prevent every incident.
They demonstrate why businesses need strong basic controls that reduce common weaknesses and make successful attacks harder.
Use the preparation exercise to improve security
Certification should create practical value.
If preparation identifies unsupported software, replace or remove it.
If too many people have administrator rights, reduce them.
If cloud services lack MFA, enable it.
If nobody knows which devices belong to the company, improve asset management.
If former employees retain accounts, strengthen the leaver process.
These improvements help protect the business regardless of the certificate.
The certificate then provides independent confirmation that your organisation meets the required baseline at the point of assessment.
Can I renew my Cyber Essentials certification through an online service?
Yes.
Cyber Essentials uses an online assessment process, and the certificate needs annual renewal.
IASME confirms that Cyber Essentials and Cyber Essentials Plus certificates expire after 12 months. Organisations need to certify again each year to maintain current status.
IASME also states that organisations need to enter their information again when renewing.
This provides an annual review of the company’s security position because systems, users and assessment questions may have changed since the previous certification.
Do not simply copy old answers without checking them.
Review:
New devices
Removed devices
New cloud services
Changes to MFA
Operating system support
New applications
User accounts
Administrator privileges
Firewall changes
Renewal becomes much easier when the organisation maintains Cyber Essentials controls throughout the year.
Keep your records after certification
Save useful information from your assessment.
Keep a copy of your answers.
Maintain your device and cloud service records.
Track major changes.
Document important account reviews.
Record any system replacements.
IASME specifically recommends retaining a copy of submitted information because applicants must complete the assessment again when they renew.
Maintaining these records also makes the next assessment less disruptive.
Build Cyber Essentials into employee processes
Certification becomes easier to maintain when security connects with everyday business activity.
When an employee joins:
Create only the access they need.
Set up MFA.
Provide secure equipment.
When somebody changes role:
Review their permissions.
Remove access that no longer makes sense.
When somebody leaves:
Disable accounts promptly.
Recover company devices.
Remove administrator access.
These simple processes stop your security position gradually becoming weaker between assessments.
Build update management into normal IT work
Do not wait until renewal to check software support.
Maintain a regular process.
Monitor the products your organisation relies upon.
Know when important suppliers plan to end support.
Replace software before support ends.
Apply relevant security fixes within the required period.
Review failed updates.
Keep an eye on devices that remain offline for long periods.
Routine maintenance turns annual certification preparation into a verification exercise rather than an emergency remediation project.
Understand Cyber Essentials Plus
Some organisations later progress to Cyber Essentials Plus.
Both schemes use the same underlying technical controls, but Cyber Essentials Plus adds independent technical testing.
If you expect a customer or tender to require Cyber Essentials Plus, tell your Certification Body early.
Preparing Cyber Essentials properly gives you a stronger foundation because technical testing will examine whether the controls operate in practice.
Do not assume that passing the verified self-assessment guarantees that every technical test will automatically succeed.
Keep your environment consistent after achieving the initial certification.
Which companies provide Cyber Essentials certification services in the UK?
Official Cyber Essentials certification comes through Certification Bodies operating within the IASME scheme.
UK Cyber Security Group confirms that it is a registered Cyber Essentials Certification Body and can guide businesses through the application process.
IASME also maintains information about Cyber Essentials certification and the assessment process.
When choosing a provider, consider more than the ability to issue the certificate.
Look for clear communication.
Ask whether the provider can help you understand scope.
Check whether it has experience with modern cloud environments.
Find out whether it can support Cyber Essentials Plus if you later require additional assurance.
A capable Certification Body should help make the assessment understandable without weakening the scheme requirements.
Which UK-based firms offer Cyber Essentials consultancy services?
Many UK cyber security companies provide Cyber Essentials advice and preparation support.
Some organisations need very little consultancy because they already have experienced internal IT staff.
Others benefit from help reviewing scope, cloud services, software support, administrator accounts, MFA and technical controls.
UK Cyber Security Group provides Cyber Essentials certification alongside additional assistance for organisations that need support through the process. Its current website confirms that it can guide applicants through certification and provide greater assistance where required.
Choose consultancy that improves the underlying security configuration.
The goal should never involve finding clever ways to make a weak environment sound compliant.
A good adviser should tell you what needs fixing, explain why and help you build a sustainable security baseline.
Common preparation mistakes
Several mistakes repeatedly create unnecessary difficulty.
One involves starting the assessment without knowing which devices and services fall inside scope.
Another involves discovering unsupported software after submission.
Businesses also overlook cloud MFA.
Some organisations assume their outsourced IT provider has already handled every requirement.
Others fail to review administrator privileges.
Another common problem involves inaccurate answers.
Do not choose the response that sounds most secure.
Choose the response that accurately describes your organisation.
If that answer reveals a compliance gap, correct the gap before submission.
Do not make certification a once-a-year event
Cyber Essentials works best when the controls remain active throughout the year.
Security can deteriorate gradually.
Employees join.
Employees leave.
New laptops arrive.
Cloud services get adopted.
Applications become unsupported.
Administrator accounts accumulate.
Firewall rules change.
Keep a light but regular review process.
A monthly or quarterly internal check of key areas can make annual renewal much easier.
The exact frequency should reflect your organisation and its rate of change.
A practical preparation checklist
Before submitting your Cyber Essentials assessment, check the following:
- You have downloaded and reviewed the current assessment questions.
- You understand the current v3.3 requirements.
- Your assessment scope accurately reflects the business.
- You know which devices fall within scope.
- You know which operating systems those devices use.
- All relevant operating systems still receive security support.
- Relevant applications still receive security support.
- You understand which cloud services employees use.
- MFA operates on applicable cloud services where available.
- Former employee accounts have been removed or disabled.
- Users have only the access they need.
- Administrator privileges have been reviewed.
- Default credentials have been replaced where relevant.
- Your firewall arrangements meet the requirements.
- Unnecessary internet exposure has been removed.
- Security updates receive appropriate management.
- Malware protection operates on relevant devices.
- Remote working arrangements have been considered.
- Your IT provider has verified technical information where necessary.
- Senior management understands what the organisation will submit.
- You have corrected known gaps before formal submission.
- You have retained useful records to support future renewal.
If several of these areas remain uncertain, complete more preparation before submitting your assessment.
Make the assessment easier by staying ready
The most effective answer to “How do I prepare Cyber Essentials Certification?” is to treat preparation as a structured review of the five technical controls.
Start with the current questions.
Define your scope.
Know your devices.
Understand your cloud services.
Remove unsupported software.
Check firewalls and secure configuration.
Review accounts and administrator access.
Enable MFA wherever the scheme requires it.
Manage security updates.
Confirm malware protection.
Give your assessor accurate answers.
Cyber Essentials gives UK businesses a practical baseline for addressing common cyber threats. The current 2026 requirements continue to focus on the same five core controls while strengthening clarity around modern environments such as cloud services.
UK Cyber Security Group provides Cyber Essentials certification and guidance through the official scheme, helping organisations work through the assessment and address security requirements before certification.
Preparation should leave your organisation in a stronger position than it started. When the process results in supported software, stronger authentication, cleaner access permissions, better account management and a clearer understanding of your IT environment, Cyber Essentials has delivered practical security value as well as recognised certification.
UK Cyber Security Group Ltd is here to help
Please check out our Free Cyber Insurance
Other blog posts, Your ISO 27001 Questions Answered, Get ISO 27001 Certified ,
If you would like to know more, do get in touch as we are happy to answer any questions. Looking to improve your cybersecurity but not sure where to start? Begin by getting certified in Cyber Essentials, the UK government’s scheme that covers all the technical controls that will provide the protection that you need to help guard against criminal attacks. Or just get in touch by clicking contact us


