
What is an IASME Cyber Essentials Certifying Body?
What is an IASME Cyber Essentials Certifying Body?
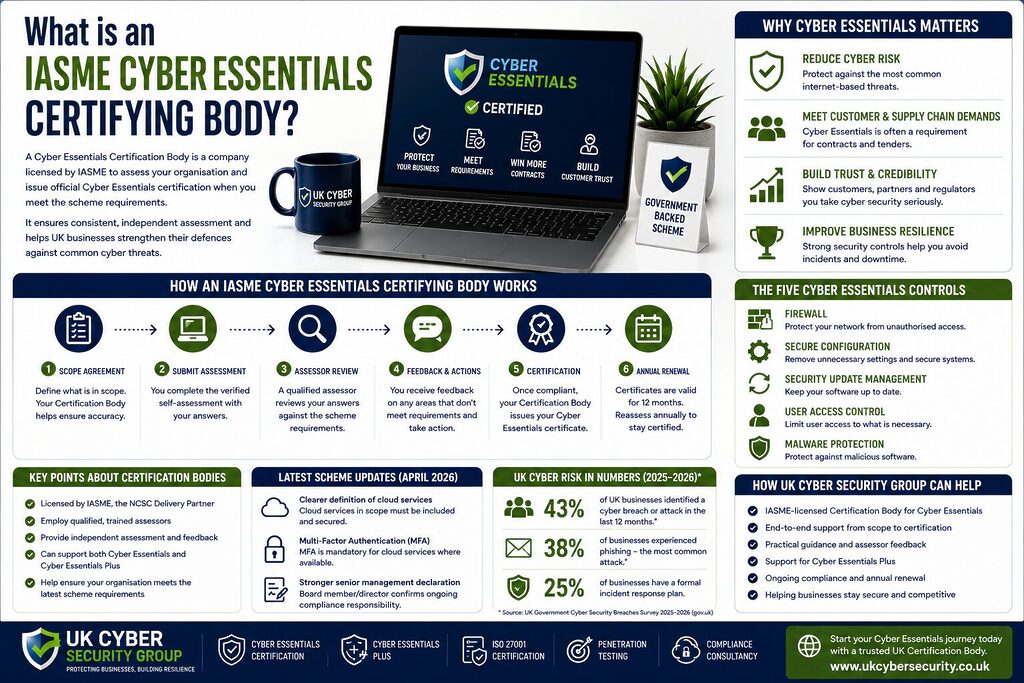
An IASME Cyber Essentials Certifying Body is a cyber security company authorised within the official Cyber Essentials scheme to assess organisations and issue Cyber Essentials certification when the required controls have been met. The formal term used by IASME is Certification Body, often shortened to CB. People may search for “Certifying Body”, but Certification Body is the terminology used throughout the official scheme.
IASME is the National Cyber Security Centre’s Delivery Partner for Cyber Essentials. IASME licenses Certification Bodies to carry out Cyber Essentials assessments, and assessors must work through one of these organisations. IASME states that Certification Bodies are based throughout the UK and Crown Dependencies and must meet defined security and quality requirements.
For a business seeking Cyber Essentials, the Certification Body provides the route into the official certification process. It reviews the answers submitted by the applicant, identifies areas that do not meet the scheme requirements, provides assessment feedback and can award certification when the organisation demonstrates compliance.
UK Cyber Security Group provides Cyber Essentials certification support for organisations that want help progressing through the assessment. Its Cyber Essentials service describes the company as a provider that helps organisations gain certification and understand the technical controls needed to protect against common cyber attacks.
The difference between IASME and a Certification Body
IASME and a Certification Body perform different roles.
IASME manages delivery of the Cyber Essentials scheme as the NCSC’s Delivery Partner. It maintains the assessor and Certification Body network, supports scheme delivery and provides resources such as the Cyber Essentials Knowledge Hub and Readiness Tool.
A Certification Body works directly with applicants.
Its role includes assessing whether an organisation meets the required Cyber Essentials criteria and issuing certification when those requirements have been satisfied. IASME describes Certification Bodies as specially trained cyber security companies that are licensed and assured to provide assessment and certification services.
This distinction matters when choosing who will assess your business.
You do not simply choose any cyber security consultancy and ask it to issue Cyber Essentials certification. Certification must come through the recognised scheme using an IASME licensed Certification Body. The NCSC confirms that Cyber Essentials assessments can only be completed by recognised Certification Bodies approved by IASME.
Why Cyber Essentials uses authorised organisations
Cyber Essentials provides a government-backed baseline for protecting organisations against common internet-based cyber threats.
The NCSC describes Cyber Essentials as the minimum cyber security standard recommended by the Government and says that the scheme centres on five technical controls.
Using licensed Certification Bodies helps maintain consistency.
A company applying for certification should receive assessment against the same scheme requirements whether it works with a provider in London, Manchester, Cardiff, Edinburgh or elsewhere in the UK.
IASME requires Certification Bodies to meet security and quality requirements and employ qualified assessors. Assessors undergo training and assessment before they can assess Cyber Essentials applications.
This structure helps businesses distinguish official certification from general cyber security advice.
A consultant can tell you what good security looks like. A recognised Certification Body can formally assess you under the Cyber Essentials scheme and issue the certification when you meet the requirements.
The assessor behind the certification
The person reviewing your Cyber Essentials application is a qualified Cyber Essentials Assessor.
IASME states that an assessor is a trained cyber security professional who evaluates whether an organisation satisfies the certification criteria. Every assessor must work for a Certification Body.
The assessor reviews the answers submitted through the verified self-assessment process.
They may ask questions when an answer needs clarification.
They can identify answers that do not demonstrate compliance.
Where necessary, the applicant may need to provide further evidence before certification can be awarded. The current Cyber Essentials Requirements for IT Infrastructure confirms that an applicant may need to supply evidence before its Certification Body can award certification.
This independent review gives Cyber Essentials more value than an internal checklist completed without external verification.
Cyber Essentials is built around five technical controls
The Cyber Essentials scheme focuses on five areas:
Firewalls
Secure configuration
Security update management
User access control
Malware protection
The NCSC states that these controls are designed to help prevent common internet-based cyber security threats.
The Certification Body checks the applicant’s responses against these requirements.
Current applications created after 27 April 2026 use Cyber Essentials Requirements for IT Infrastructure v3.3. IASME confirmed that this version applies to assessment accounts created after that date.
The organisation remains responsible for meeting every applicable requirement within its agreed scope.
The Certification Body helps establish your assessment scope
Scope is one of the most important parts of Cyber Essentials.
Before the assessment begins, the organisation needs to establish the boundary of the certification and determine which infrastructure sits inside it.
The current NCSC requirements state that applicants must agree the scope with their Certification Body before assessment begins.
Scope can include:
Business devices
Servers
Networks
Cloud services
User accounts
Remote workers
Internet gateways
Software used for organisational purposes
The 2026 requirements strengthened the emphasis on scope transparency. IASME now requires applicants to identify excluded infrastructure and provide additional information about legal entities covered by certification.
A knowledgeable Certification Body can therefore help make sure the scope accurately reflects the organisation before the formal assessment progresses.
Cloud services now need particular attention
Cloud services play a major role in modern Cyber Essentials assessments.
Businesses commonly rely on Microsoft 365, Google Workspace, customer relationship management platforms, accounting services, cloud storage and other online applications.
The 2026 Cyber Essentials update added a clearer definition of cloud services and confirmed that relevant cloud services cannot simply be removed from scope. IASME also strengthened the marking requirements around multi-factor authentication.
IASME states that multi-factor authentication is mandatory for cloud services where it is available under the current requirements. Failure to implement it where required can cause an assessment to fail.
A Certification Body can help an applicant understand how these requirements apply to the services it actually uses.
What are the key requirements for achieving Cyber Essentials certification?
To achieve Cyber Essentials certification, an organisation needs to meet the applicable requirements across the five technical controls and correctly define its scope.
Firewalls should protect devices and networks from unwanted internet access.
Secure configuration requires organisations to remove unnecessary settings, services and accounts that could create avoidable weaknesses.
Security update management requires supported software and appropriate action on relevant security updates.
User access control requires businesses to give people only the access they genuinely need and manage administrator privileges carefully.
Malware protection requires appropriate safeguards against malicious software.
The applicant must also accurately describe the environment covered by the certification and answer the verified self-assessment questions truthfully.
The current requirements make clear that the applicant carries responsibility for meeting every relevant requirement within the agreed scope.
A board member or director signs the declaration associated with the verified self-assessment. IASME strengthened this declaration in 2026 so that senior management acknowledges the organisation’s responsibility to maintain Cyber Essentials controls throughout the certificate period.
Cyber Essentials is not simply a questionnaire
Businesses sometimes assume that Cyber Essentials involves filling in an online questionnaire and receiving a certificate automatically.
The process is more meaningful than that.
The answers describe how your organisation protects its IT environment. A qualified assessor reviews those answers against the scheme requirements.
IASME’s current FAQ explains that applicants receive feedback when an answer does not demonstrate compliance. This feedback can help the organisation understand what needs correcting before a later attempt.
Unsupported software within scope remains a particularly important issue. IASME states that an organisation using unsupported software within its assessment scope will not achieve Cyber Essentials certification.
This is why preparation matters.
How can I prepare my small business for Cyber Essentials assessment?
Start with an accurate picture of the technology your organisation uses.
Record your computers, laptops, mobile devices, servers, routers, cloud services and relevant software.
Check whether every operating system and application inside scope still receives security support.
Review administrator accounts and remove privileges that employees do not need.
Confirm that multi-factor authentication operates on relevant cloud services.
Review security updates and make sure your organisation can demonstrate that supported software receives appropriate attention.
Look at firewall arrangements and remove unnecessary internet exposure.
Confirm that malware protection operates on relevant devices.
You should also identify cloud services that employees use for business purposes and make sure they appear correctly within the scope.
IASME and the NCSC provide a free Cyber Essentials Readiness Tool. IASME says the tool uses interactive questions to help organisations understand their current position and produces guidance based on the answers supplied.
A Certification Body can also provide guidance around the assessment and explain how questions relate to your organisation.
Advice and certification are not quite the same thing
A business may need advice before it is ready for certification.
That help might come from a Certification Body, a cyber security consultant or an NCSC Assured Cyber Advisor.
IASME explains that Cyber Advisors help smaller organisations implement the Cyber Essentials technical controls, while organisations wanting formal certification still need to apply through a Cyber Essentials Certification Body. Many Cyber Advisors work closely with Certification Bodies, and some organisations perform both roles.
This distinction gives businesses flexibility.
If your company already has strong technical knowledge, you may only need assessment and certification.
If you have gaps in your security arrangements, consultancy before assessment may save considerable effort.
What software solutions support compliance with Cyber Essentials standards?
Cyber Essentials does not depend on one specific software platform.
Different solutions can support different requirements.
Endpoint management systems can help organisations identify devices and monitor security updates.
Identity platforms can help manage users, administrators and multi-factor authentication.
Endpoint security systems can support malware protection.
Asset management solutions can help maintain reliable information about computers and applications.
Cloud administration portals can provide evidence relating to authentication, user accounts and security settings.
Vulnerability management platforms can help businesses identify weaknesses that require attention.
Password managers can help employees maintain unique credentials.
Compliance platforms can help organise scope information, evidence, actions and review activity.
No software solution can guarantee Cyber Essentials certification on its own.
The organisation still needs to meet the actual scheme requirements and answer the assessment accurately.
What happens when an assessor finds a problem?
A non-compliant answer does not necessarily mean the process becomes unmanageable.
IASME states that applicants receive feedback on areas that do not fully comply. The assessment report contains the submitted answers and assessor comments against responses considered non-compliant.
That feedback is useful because it turns certification into a practical security exercise.
Instead of simply receiving a rejection, the organisation can understand the weakness and address it.
Examples might include:
Unsupported software
Missing multi-factor authentication
Excessive administrator rights
Incorrect scope information
Weak security update arrangements
Unnecessary internet exposure
A good Certification Body should explain the issue clearly without disguising the technical requirement behind unnecessary jargon.
Cyber Essentials and Cyber Essentials Plus
Cyber Essentials and Cyber Essentials Plus use the same underlying technical controls, but the assurance process differs.
Cyber Essentials uses an independently verified self-assessment.
Cyber Essentials Plus adds technical testing.
IASME explains that Cyber Essentials Plus includes a technical audit of in-scope systems, including vulnerability assessment and testing of a representative sample of relevant devices and infrastructure.
Not every Cyber Essentials Certification Body necessarily carries out Cyber Essentials Plus work. IASME maintains Certification Bodies that have the relevant training and licensing for the Plus assessment.
If you expect to progress to Cyber Essentials Plus, ask your provider about its Plus capability at the start.
Can I renew my Cyber Essentials certification through an online service?
Yes. Cyber Essentials uses an online assessment process and certification requires annual renewal.
IASME states that Cyber Essentials and Cyber Essentials Plus certificates expire after 12 months. Organisations need to complete the certification process again to maintain a current certificate.
Renewal should not involve blindly copying the previous year’s answers.
Technology changes.
Employees join and leave.
Cloud platforms change.
Software reaches the end of support.
New accounts appear.
Networks evolve.
The annual assessment therefore provides a useful opportunity to review your current security position.
IASME confirms that organisations need to enter their information again when recertifying because this process acts as an annual cyber security review.
UK Cyber Security Group provides Cyber Essentials certification services and can support organisations through both initial assessment and later renewal activity.
Choosing a Certification Body that fits your business
Certification Bodies all work within the same Cyber Essentials framework, but the service experience can differ.
Consider whether the provider:
Explains requirements clearly
Responds promptly to assessment questions
Understands cloud environments
Has experience with smaller organisations
Can support Cyber Essentials Plus if required
Offers consultancy where your organisation needs help
Understands remote working
Can help clarify assessment scope
Provides practical assessor feedback
Has wider cyber security expertise
The cheapest route is not always the right one when an organisation needs substantial assistance, although a straightforward company with a well-managed environment may prefer a streamlined service.
UK Cyber Security Group positions its Cyber Essentials service around making certification straightforward and accessible for UK businesses.
Which companies provide Cyber Essentials certification services in the UK?
Cyber Essentials certification services are provided through organisations licensed by IASME as Certification Bodies.
IASME maintains a Certification Body directory that allows businesses to search for recognised providers across the UK and Crown Dependencies.
UK Cyber Security Group provides Cyber Essentials certification services and supports organisations through the assessment process.
When comparing providers, confirm that the organisation operates through the official IASME scheme rather than assuming that any cyber consultancy can issue a valid certificate.
The NCSC states that Cyber Essentials assessment must be carried out by recognised Certification Bodies approved by IASME.
Which UK-based firms offer Cyber Essentials consultancy services?
A range of UK cyber security organisations provide consultancy around Cyber Essentials.
IASME itself notes that Certification Bodies may provide consultancy to help applicants understand the assessment questions and how those questions relate to the organisation.
NCSC Assured Cyber Advisors provide another recognised route for organisations that need practical help implementing the technical controls before certification. IASME states that Cyber Advisors specialise in helping smaller organisations identify gaps and take action towards Cyber Essentials.
UK Cyber Security Group provides Cyber Essentials certification together with wider cyber security and compliance support.
A useful consultancy provider should focus on improving your actual security rather than merely producing attractive questionnaire answers.
The goal should be to reach compliance because the controls work.
Why Cyber Essentials matters to UK businesses
Cyber attacks remain common among UK organisations.
The UK Government’s Cyber Security Breaches Survey 2025 to 2026 found that 43 per cent of businesses identified a cyber breach or attack during the previous 12 months. Phishing affected 38 per cent of businesses.
The survey also found that 24 per cent of businesses reported having controls across all five areas associated with Cyber Essentials, while 5 per cent reported holding Cyber Essentials certification. The proportion holding certification had increased from the previous year.
These figures show an important distinction.
Many companies have some security measures.
Fewer have independently demonstrated that those controls meet the Cyber Essentials scheme requirements.
Certification provides a recognised way to show customers, partners and procurement teams that the business has worked through that process.
Cyber Essentials can support tender opportunities
The NCSC notes that a growing number of organisations require suppliers to hold Cyber Essentials before they can bid for work.
IASME also states that Cyber Essentials appears in a large number of central government contracts and an increasing number of local government contracts.
For suppliers, certification therefore provides both a security benefit and a commercial assurance benefit.
A customer can see that an independent assessor has reviewed the organisation’s self-assessment against a government-backed baseline.
The 2026 requirements place greater emphasis on ongoing security
Cyber Essentials remains a point-in-time certification, with the certificate date representing the assessment point. IASME clarified this position in the April 2026 update.
However, the 2026 declaration also reinforces that organisations should maintain compliance with the Cyber Essentials controls throughout the certificate period.
This is an important message for businesses.
Cyber Essentials should not become a once-a-year scramble.
Maintain supported software.
Keep administrator accounts under control.
Continue applying security updates.
Maintain multi-factor authentication.
Review new cloud services.
Update your asset information.
When annual renewal arrives, a business that maintains its controls should find the process far easier.
What a good Certification Body should give you
A strong Certification Body relationship should provide clarity.
You should understand:
What sits within scope
Which requirements apply
Why an answer does not comply
What evidence may be needed
What happens after submission
How certification gets issued
When renewal becomes due
What Cyber Essentials Plus would involve
The provider should not weaken requirements simply to make certification easier.
Its role involves protecting the integrity of the scheme as well as supporting the applicant.
That independent assessment is part of what gives the certificate value.
A practical checklist before choosing your provider
Before selecting a Cyber Essentials Certification Body, ask:
Is the company licensed through IASME?
Does it employ qualified assessors?
Can it explain the current 2026 requirements?
Does it understand cloud services?
Can it help clarify scope?
Does it support Cyber Essentials Plus if we need it?
Can it provide consultancy where appropriate?
Does it communicate in plain English?
Will we receive useful feedback if an answer fails?
Can it support future annual renewal?
Does it understand our business environment?
Can it provide wider security help if the assessment identifies a larger problem?
These questions can help you choose a provider based on service quality as well as certification capability.
The Certification Body is your official route to Cyber Essentials
An IASME Cyber Essentials Certification Body provides the independent assessment route that turns your organisation’s technical security controls into recognised Cyber Essentials certification.
IASME manages delivery of the scheme for the NCSC, while licensed Certification Bodies work directly with applicants. Assessors review submissions, provide feedback and issue certification when the requirements have been met.
The current scheme uses five core technical controls and, for assessment accounts created after 27 April 2026, the Requirements for IT Infrastructure v3.3.
For UK businesses, choosing the right Certification Body can make the process clearer and easier to manage without reducing the security standard.
UK Cyber Security Group provides Cyber Essentials certification and wider compliance support for organisations that want help understanding and completing the process.
The best outcome is not simply receiving a certificate. It is reaching certification with a clearer understanding of your technology, fewer avoidable weaknesses and practical controls that continue protecting the organisation after the assessment has finished.
UK Cyber Security Group Ltd is here to help
Please check out our Free Cyber Insurance
Other blog posts, Your ISO 27001 Questions Answered, Get ISO 27001 Certified ,
If you would like to know more, do get in touch as we are happy to answer any questions. Looking to improve your cybersecurity but not sure where to start? Begin by getting certified in Cyber Essentials, the UK government’s scheme that covers all the technical controls that will provide the protection that you need to help guard against criminal attacks. Or just get in touch by clicking contact us


