
What to do if my details are on the dark web?
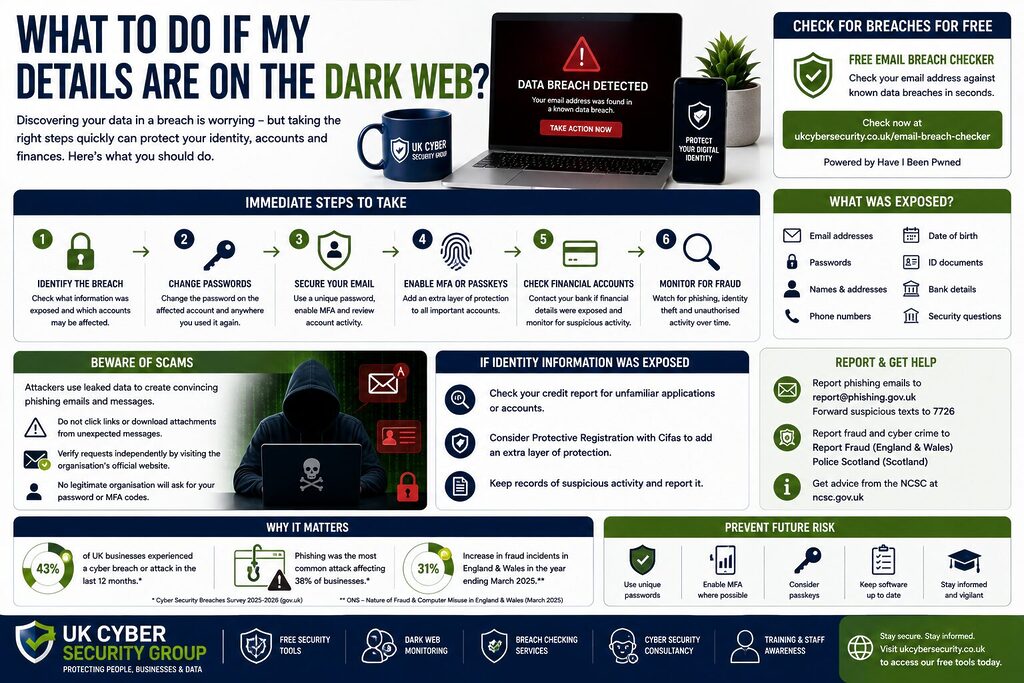
What to do if my details are on the dark web?
Finding out that your email address, password or personal information has appeared in a known data breach can be unsettling, but the most important thing is to act quickly and methodically.
A breach result does not automatically mean that criminals have accessed every account you own. It means information associated with you has appeared in a compromised dataset and you should assess what was exposed, secure affected accounts and watch for signs of misuse.
UK Cyber Security Group provides a free email breach checker that allows you to check an email address against known data breaches. The service queries Have I Been Pwned and recommends changing affected passwords and enabling additional authentication when a match appears.
It is important to understand the limitation of any checker. A match confirms that an identifier appeared in information known to the service. A clean result cannot prove that your information has never been stolen, because criminals may hold information that has not become available to breach databases or security researchers.
The practical response therefore combines breach checking with strong account security, fraud monitoring and sensible caution around unexpected emails, calls and messages.
Act quickly, but work through the problem in order
The first thing to establish is exactly what information may have escaped.
An exposed email address creates a different level of risk from an exposed password, passport record, bank detail or business administrator credential.
Do not start changing random settings without first understanding what happened. Make a short record of the breach result and identify the service associated with it.
Ask:
Which account was affected?
When did the breach happen?
Which information fields were exposed?
Was a password included?
Do I still use that password?
Have I reused a similar password anywhere else?
Does the email address control password resets for important accounts?
Does the information relate to my employer?
Could the exposed information help someone impersonate me?
This assessment helps you prioritise the accounts that need attention first.
The NCSC advises people affected by data breaches to change compromised passwords, check whether they reused those credentials elsewhere and remain alert for scams that use exposed personal information.
What is a data breach checker?
A data breach checker searches known compromised records for an identifier such as an email address.
The UK Cyber Security Group free email breach checker sends the email address you enter to Have I Been Pwned, a widely used database of known data breaches. The service then reports whether that address appears in known compromised information.
A checker can help answer an important question: has this email address appeared in a breach that security researchers already know about?
It should not ask for the password you currently use. You should never enter an active password simply because a website claims it needs the credential to check whether you have suffered a breach.
A breach checker also differs from continuous dark web monitoring. A one-off check looks at available breach records at the time of your search. Monitoring services can repeatedly look for new exposure associated with a business or account.
UK Cyber Security Group also provides dark web monitoring for organisations that want ongoing checks for compromised company credentials. Its service focuses on information such as email addresses, usernames, passwords, personal information and bank information that may have become exposed.
If your password has appeared, change it first
An exposed password deserves immediate attention.
Change the password on the affected account if the account still exists.
Next, identify every other account where you used the same password. Change those credentials as well.
Do not simply add another number or symbol to the compromised password. Create a genuinely different credential.
Password reuse creates a serious problem because attackers routinely try stolen email and password combinations against unrelated services. The NCSC refers to this practice as credential stuffing and recommends avoiding password reuse across accounts.
For example, imagine that an online retailer suffered a breach several years ago and exposed your email address and password.
You may no longer use the retailer.
However, if you used the same password for Microsoft 365, Gmail, Facebook, cloud storage or another service, criminals can still try that stolen combination against those accounts.
The age of the breach does not make a reused credential safe.
Protect your email account before almost anything else
Your primary email account often provides access to the rest of your digital identity.
Banks, retailers, cloud platforms, social networks and business systems commonly use email for password resets, security notifications and account recovery.
If a criminal gains access to the email account, they may be able to reset passwords elsewhere.
Protect the account with a unique password that you do not use anywhere else.
Turn on multi-factor authentication or two-step verification.
Review the recovery email address and telephone number.
Check recently logged-in devices or sessions.
Remove any device you do not recognise.
Look for unfamiliar mail forwarding rules.
Review connected applications.
Check your sent folder and deleted messages for activity you did not create.
The NCSC strongly recommends two-step verification because it gives accounts another layer of protection when a password becomes known to an attacker.
Consider passkeys where your important services support them
Many major online services now support passkeys as an alternative to traditional passwords.
The NCSC published updated analysis in April 2026 stating that passkeys provide stronger resistance against common attacks including phishing and credential reuse than traditional password-based approaches.
You do not need to move every account immediately.
Start with important accounts such as email, cloud services and other accounts that hold sensitive information.
The key principle remains the same. Reduce your dependence on credentials that criminals can reuse after a breach.
How can get an email breach checker for free?
UK Cyber Security Group provides a free email breach checker on its website.
You enter the email address you want to check and the service compares it with known breach information through Have I Been Pwned. UK Cyber Security Group states that the checker is free to use and that any valid email address can be checked.
You do not need to search criminal forums or hidden services yourself.
That is an important safety benefit. Trying to investigate stolen data personally can expose you to malicious downloads, scams, disturbing content or unreliable claims.
Use a reputable checker and concentrate on securing your accounts.
UK Cyber Security Group also provides several other free security tools alongside its email breach checker.
What is the best free email breach check?
A useful free breach checker should tell you clearly what source it searches, avoid asking for your active password and explain what you should do if it finds a match.
UK Cyber Security Group’s free checker provides a straightforward option for a UK user because it checks the email address against the Have I Been Pwned breach database and gives immediate advice following a positive result.
Avoid any service that claims it can guarantee that your personal information does not exist anywhere on hidden criminal networks.
No checker has complete visibility into every private criminal database, closed forum, stolen device or unpublished breach.
A clean search result means the service did not identify the address in the information it searched. Continue to use strong authentication and unique credentials even when the search finds nothing.
A leaked email address still matters without a password
You may discover that a breach exposed your email address but not a password.
Do not ignore the result.
An email address can help criminals build more convincing phishing campaigns.
They may combine it with information from company websites, social media, public records or another breach.
A message becomes much more persuasive when the sender already knows your name, employer, role or a service that you genuinely use.
The UK Government’s Cyber Security Breaches Survey 2025 to 2026 found that 38 per cent of businesses experienced phishing during the previous 12 months, making it the most commonly reported cyber attack among businesses.
Treat unexpected messages carefully even when they contain accurate information about you.
Accuracy does not prove that the sender is genuine.
Expect more convincing phishing after a breach
Criminals frequently use leaked information to make scams feel personal.
You might receive a message that names a service you genuinely used or refers to an old address, telephone number or employer.
That information may have come from a breach rather than from direct access to your current account.
Do not follow an unexpected link simply because the message contains information that only seems private.
Open the service independently through its normal website or application.
Verify urgent payment requests through another trusted route.
Be particularly careful with:
Password reset requests you did not initiate
Requests to confirm identity information
Messages about account suspension
Unexpected invoices
Bank detail changes
Parcel messages
Tax-related messages
Requests from senior employees asking for urgent payment
Messages containing old passwords
Criminals sometimes include an old password specifically to frighten recipients into believing they have deeper access than they really do.
Do not pay someone simply because they know an old password
One common scam tells the recipient that criminals have compromised their device, recorded them or obtained private information.
The message may include an old password as supposed proof.
That password may simply have come from an earlier breach.
Do not assume the wider claims are true solely because the sender knows an old credential.
Secure the affected accounts and report the message.
The NCSC provides a Suspicious Email Reporting Service for scam emails and recommends forwarding suspicious texts to 7726.
If bank or card information appears, contact the provider
Financial information requires prompt attention.
Contact your bank, card provider or relevant financial organisation through its official contact route.
Explain that your information may have become compromised and follow its fraud prevention guidance.
Review recent transactions.
Check for unfamiliar payments, transfers or new beneficiaries.
Continue monitoring activity because criminals may not use stolen information immediately.
Do not use telephone numbers included in unexpected messages claiming to come from your bank. Use the number printed on your card, shown in your banking application or published through the bank’s official service.
The ICO advises people facing identity theft to inform their bank, building society and card providers about unusual transactions and to review their credit file for suspicious applications.
If identity information appears, think beyond passwords
A breach may expose much more than account credentials.
Information can include:
Your full name
Home address
Previous addresses
Date of birth
Telephone number
Identification document information
Employment information
Security question answers
Financial information
Identity information can help criminals impersonate you even when they do not know your current passwords.
Check your credit records for applications you do not recognise.
Watch for letters relating to financial products or accounts you did not request.
Keep evidence of suspicious activity.
Report lost or compromised official documents to the organisation that issued them where appropriate.
The ICO recommends these steps when someone may face identity theft.
Identity fraud remains a significant UK problem. Cifas reported that almost 130,000 identity fraud cases appeared in the first half of 2026, representing 59 per cent of fraud-risk cases recorded in its National Fraud Database during that period.
Consider additional identity protection when the exposure is serious
Cifas operates Protective Registration for people who believe criminals may misuse their identity.
The service places a warning against the registered person’s details in the Cifas National Fraud Database. Participating organisations can then perform additional checks when someone attempts to use those details for financial products or services.
Protective Registration does not guarantee that identity fraud cannot occur. Cifas explicitly states that it does not prevent every form of fraud or identity theft.
Consider the option when sensitive identity information has become exposed or when you see signs that someone has started impersonating you.
Can I use a data breach checker UK?
Yes. UK individuals and organisations can use reputable breach checking services to identify known exposure associated with an email address.
UK Cyber Security Group provides a free checker aimed at helping users identify whether an email address appears in known compromised records.
Using a checker does not replace wider security.
Think of the result as an alert.
A positive match tells you to investigate and strengthen affected accounts.
A negative match tells you that the searched source did not identify a known exposure, but you should still protect your accounts properly.
For businesses, individual checking can also support a broader security programme involving user access control, multi-factor authentication, staff awareness, monitoring, vulnerability management and incident response.
If a work email appears, tell your organisation
Do not treat compromised work credentials purely as a personal problem.
Inform your IT team, security team, manager or designated support provider.
The business may need to:
Reset the password
Revoke existing login sessions
Check multi-factor authentication
Review sign-in history
Examine administrator permissions
Search for suspicious inbox rules
Review related accounts
Check other employee exposure
Monitor unusual activity
Investigate whether the account suffered actual compromise
An exposed work password can create risk beyond one employee.
Attackers may use access to impersonate staff, target suppliers, request fraudulent payments or move towards more sensitive systems.
Early reporting gives the organisation more options.
If you run the business, check whether the incident affects personal data
When an organisation discovers that customer or employee personal information has become exposed, it needs to assess the incident properly.
The ICO advises organisations to establish what information was affected, how many people could face harm and what consequences could follow.
Contain the problem first where possible.
Secure compromised accounts.
Remove unauthorised access.
Preserve relevant records.
Establish what happened.
Identify affected information and people.
Assess potential harm.
Document the decision-making process.
Where a personal data breach creates the level of risk that requires ICO notification, UK data protection rules generally require the organisation to notify the ICO without undue delay and, where feasible, within 72 hours of becoming aware of it.
Seek appropriate professional guidance when the facts or reporting duties remain unclear.
Search for the affected account, not the entire internet
People often react to a dark web warning by trying to remove their information from everywhere.
That usually sets an unrealistic goal.
Once criminals copy data, you cannot reliably guarantee its deletion from every private collection.
Focus instead on making the stolen information less useful.
If a password leaked, replace it.
If an account became compromised, revoke access.
If identity information leaked, watch for fraud.
If bank information leaked, contact your provider.
If business credentials leaked, investigate the account and associated systems.
If personal data belonging to others leaked, follow your incident process and assess regulatory obligations.
This approach reduces practical risk rather than chasing copies of information that you cannot control.
Which companies provide dark web email checker in the UK?
UK Cyber Security Group provides a free email breach checker for individuals and businesses. The service searches the submitted email address against known breach information through Have I Been Pwned.
The company also provides ongoing dark web monitoring aimed at organisations that want broader visibility of leaked company credentials and personal information.
Other cyber security and identity protection providers offer monitoring services, so examine their methodology before choosing one.
Ask:
Which sources does the service monitor?
Does it search known breach databases?
Does it provide continuous monitoring?
How does it protect the information you submit?
How quickly does it alert you?
Does it explain what information appeared?
Does it provide practical remediation guidance?
Can it support a business response when employee credentials appear?
No legitimate provider should claim complete visibility into every criminal forum or private dataset.
Which UK-based firms offer data breach check services?
UK Cyber Security Group offers a free email breach checker as well as wider dark web monitoring services for organisations.
UK businesses can also obtain breach checking and monitoring support from cyber security consultancies, managed security providers, identity protection specialists and threat intelligence providers.
Choose support according to the problem you need to solve.
A personal user may only need a quick email check and clear remediation advice.
A business may need continual domain monitoring, account security reviews, threat monitoring, employee awareness, incident response and wider cyber security controls.
UK Cyber Security Group offers additional services aimed at helping businesses identify and manage cyber security exposure alongside its free checking tools.
Report phishing rather than simply deleting it
Reporting scams can help disrupt criminal infrastructure.
The NCSC currently advises users to forward suspicious emails to report@phishing.gov.uk and suspicious text messages to 7726.
If you have lost money or suffered a cyber crime, use the appropriate reporting route.
Report Fraud replaced the previous Action Fraud reporting service during late 2025. Government guidance directs victims in England and Wales to Report Fraud, while National Crime Agency guidance also directs people in Northern Ireland there. People in Scotland should report fraud or cyber crime through Police Scotland.
Keep copies of useful evidence before deleting messages.
This may include screenshots, dates, transaction information and relevant correspondence.
Watch for fraud even after you have changed passwords
Changing a password stops criminals from using that credential in the future, but it cannot reverse every consequence of the original breach.
They may already know:
Your name
Employer
Home address
Telephone number
Services you use
Old account information
Other identifying details
That information can remain useful for social engineering.
Stay cautious when someone contacts you unexpectedly and appears to know a surprising amount about you.
Verify them independently.
Never assume that possession of personal information proves identity.
Businesses should consider domain-wide monitoring
Checking one email address helps one user.
A company may need a wider view.
Several employees could have used company addresses with unrelated external services that later suffered breaches.
A criminal could use those records to identify staff, target high-value roles or create convincing impersonation attempts.
Ongoing monitoring can help organisations identify new credential exposure sooner.
Give responsibility for alerts to a named person or security provider.
Define what happens when a match appears.
A useful response process might include checking whether the credential remains active, notifying the account owner, forcing a reset when necessary, reviewing authentication, examining suspicious activity and documenting the result.
Monitoring has little value when alerts sit unread in an inbox.
Use unique passwords to contain future breaches
Data breaches will continue to happen at organisations you do business with.
You cannot personally control the security of every retailer, application, forum or cloud provider.
You can control whether one provider’s breach unlocks your other accounts.
Use a unique credential for every important service.
A password manager can make this easier by creating and storing credentials without forcing you to remember all of them.
The NCSC recommends password managers and warns against password reuse because reuse gives attackers opportunities to move from one compromised service to another.
Treat your email account as a high-value asset
For many people, email deserves stronger protection than almost any other online account.
It provides account recovery for dozens of other services.
Apply stronger controls to it.
Use a unique credential.
Use multi-factor authentication or a passkey where supported.
Review login activity.
Keep recovery details current.
Remove old forwarding rules.
Do not share the account.
Do not approve unexpected authentication requests.
An unexpected authentication prompt may indicate that someone already knows your password.
Reject it and investigate.
Never ignore an old breach because it happened years ago
Old information can remain useful.
A password from five years ago matters if you still use it.
An old home address can help answer identity questions.
A previous telephone number may connect several breach records together.
An old employer may help a criminal construct believable social engineering.
Treat the value of the information according to whether criminals can still use it, rather than according to the date of the breach.
A practical response checklist
When a checker finds your information, follow this order:
First, identify the affected service and information.
Next, change any exposed password that still works.
Replace the same or similar password anywhere else you used it.
Secure your main email account.
Enable multi-factor authentication or stronger authentication methods.
Review active sessions and recovery settings.
Check for suspicious account activity.
Contact your bank when financial details may face risk.
Check credit records when identity information has become exposed.
Tell your employer when company credentials appear.
Stay alert for targeted phishing and impersonation.
Report suspicious emails and messages.
Record what you changed.
Continue monitoring important accounts.
Run another breach check periodically because new breach information can emerge later.
This approach converts a worrying discovery into a controlled security response.
Why this matters to UK businesses
Cyber incidents remain common across the UK.
The Government’s Cyber Security Breaches Survey 2025 to 2026 found that 43 per cent of businesses identified a breach or cyber attack in the previous 12 months. Phishing affected 38 per cent of businesses.
Separate ONS research published in March 2026 estimated 4.2 million fraud incidents in England and Wales for the year ending March 2025, an increase of 31 per cent compared with the previous survey period.
These figures demonstrate why exposed personal information deserves attention.
Criminals do not always need sophisticated technical exploits. Stolen credentials, impersonation and social engineering can give them a simpler route.
Make the stolen information less valuable
You cannot always control how your information escaped or where criminals copied it.
You can control much of what happens next.
Replace compromised credentials.
Protect email accounts.
Enable stronger authentication.
Review financial activity.
Watch for identity fraud.
Report work-related exposure.
Treat unexpected messages with caution.
Use reputable breach checking rather than exploring criminal spaces yourself.
UK Cyber Security Group’s free email breach checker gives UK users a simple way to check whether an email address appears in known breach records through Have I Been Pwned.
For businesses that need greater visibility, UK Cyber Security Group also offers ongoing dark web monitoring designed to identify compromised company credentials and other exposed information.
Finding your details in a breach does not mean criminals will definitely harm you. It does mean that you should treat those details as potentially compromised and act before attackers get an opportunity to turn old information into a new incident.
UK Cyber Security Group Ltd is here to help
Please check out our Free Cyber Insurance
Other blog posts, Your ISO 27001 Questions Answered, Get ISO 27001 Certified ,
If you would like to know more, do get in touch as we are happy to answer any questions. Looking to improve your cybersecurity but not sure where to start? Begin by getting certified in Cyber Essentials, the UK government’s scheme that covers all the technical controls that will provide the protection that you need to help guard against criminal attacks. Or just get in touch by clicking contact us


