
What can I do if my details are on the dark web?
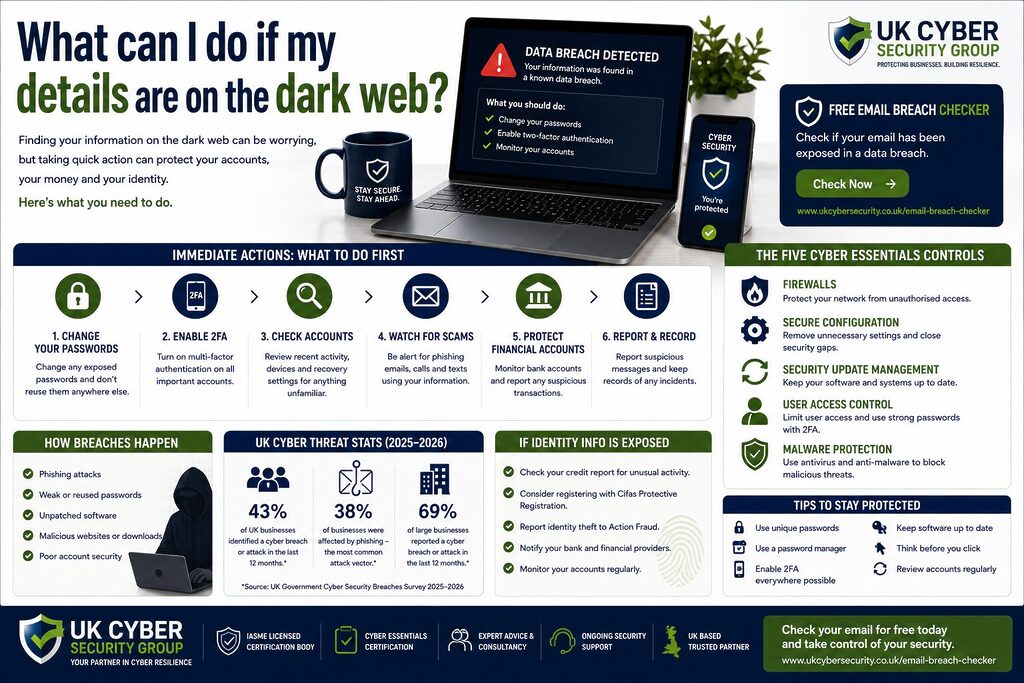
What can I do if my details are on the dark web?
Discovering that your email address, password or personal information has appeared in a data breach can feel worrying, but a positive result does not automatically mean that criminals control your accounts or have successfully used your identity. It means information connected with you has appeared in data known to have been compromised, so you should assess what has been exposed and take sensible action.
UK Cyber Security Group provides a free email breach checker that allows individuals and businesses to check an email address against known data breaches. The service queries Have I Been Pwned and tells users when the submitted email address appears in known compromised information. UK Cyber Security Group recommends changing affected passwords and enabling two-factor protection on accounts that use the same credentials.
Taking action quickly can greatly reduce the value of stolen information. You can replace passwords, secure your main email account, strengthen authentication, review financial activity and watch for targeted scams.
A breach checker cannot provide complete visibility of every criminal database or stolen record. A clean result therefore does not prove that information has never been compromised. Good account security remains important whether the search finds a breach or not.
Start by finding out exactly what was exposed
Not every breach creates the same level of risk.
An exposed email address deserves attention, but an exposed password, bank record or identity document may demand more urgent action.
Start by identifying the organisation connected with the breach and ask what information attackers obtained.
The National Cyber Security Centre advises people to contact the affected organisation through its official website or another trusted route rather than following contact details contained in an unexpected message. The organisation should be able to confirm whether a breach occurred, how it affected you and what action you may need to take.
Ask the following questions:
Was my email address exposed?
Was a password involved?
Do I still use that password?
Did I use that password on another account?
Was my telephone number exposed?
Did the breach include my home address?
Did it include financial information?
Did it include identity information?
Does the affected account belong to my employer?
Have I noticed any unusual account activity?
The answers help you decide what to tackle first.
What is a data breach checker?
A data breach checker searches known compromised information for an identifier such as your email address.
UK Cyber Security Group’s free email breach checker compares the address you enter with information available through Have I Been Pwned. The website states that the checker can identify whether an email address and associated credentials appear in known data breaches.
You should not need to provide your current password to check an email address.
Be cautious if a website asks you to submit an active password simply to determine whether it has leaked. A reputable email breach search can work from the email address without asking you to disclose the credential that currently protects the account.
A positive result should act as a warning that information connected with your address has appeared in compromised records.
A negative result only means that the search did not find your address in the information currently available to that service.
Change an exposed password immediately
If the breach involved a password that you still use, replace it.
The NCSC advises people who have disclosed or lost a password to change it on any other accounts where they use the same credential.
Do not make a small change such as adding another number to the end.
Create a genuinely different password.
Password reuse creates one of the biggest problems after a breach. Criminals know that people often reuse the same login credentials across several services. They can take a password stolen from one website and try it against email, shopping accounts, cloud platforms and other services.
This practice can turn an old breach involving an unimportant account into a current security problem.
A breach at a retailer you stopped using years ago may still matter if the password from that account remains active elsewhere.
Secure your main email account
Your email account should receive particularly strong protection because many other services use email for password resets and security notifications.
If an attacker gets into your email, they may gain opportunities to reset passwords elsewhere.
Use a unique password that you do not share with any other account.
Enable multi-factor authentication.
Review recovery addresses and telephone numbers.
Check which devices currently have access.
Look for sessions you do not recognise.
Review forwarding rules.
Check your sent messages and deleted messages.
Remove unfamiliar connected applications.
The NCSC specifically advises users recovering compromised accounts to check email filters and forwarding rules because criminals can create forwarding rules that silently send them copies of incoming messages.
These checks matter even if you can still sign in normally.
An attacker may attempt to remain unnoticed rather than immediately locking you out.
Turn on multi-factor authentication
Multi-factor authentication adds another barrier between an attacker and your account.
A stolen password becomes much less useful when the attacker also needs another approved factor.
Prioritise important accounts such as:
Business cloud platforms
Online banking
Cloud storage
Social networks
Customer portals
Administrator accounts
Where supported, passkeys can provide another strong authentication option.
The NCSC recommends stronger authentication because passwords can become compromised through phishing, breaches and reuse.
Do not approve an unexpected authentication request.
An unexpected prompt can indicate that somebody already knows your password and is trying to complete the login.
How can get an email breach checker for free?
UK Cyber Security Group provides a free email breach checker through its website.
You can enter an email address and check it against known breach information. UK Cyber Security Group confirms that the service is free and accepts valid personal or business email addresses.
The checker queries Have I Been Pwned rather than requiring you to visit criminal websites yourself.
That provides a much safer way to investigate known exposure.
Searching criminal forums or hidden services yourself provides little practical advantage and may expose you to scams, malicious files or unreliable information.
Use a reputable breach checker and concentrate on reducing the risk created by the result.
What is the best free email breach check?
A useful breach checker should clearly explain what it searches, what a positive result means and what the user should do next.
UK Cyber Security Group’s checker provides a practical UK option because it checks submitted email addresses against the Have I Been Pwned database and gives advice when known exposure appears.
The NCSC also identifies Have I Been Pwned as an example of a service people can use to check whether their details have appeared in public data breaches.
No checker can guarantee complete visibility into every stolen database held by criminals.
Judge a service by its transparency and practical value rather than dramatic claims about seeing everything on the dark web.
Check whether anyone has accessed your accounts
A breach result tells you that information appeared in compromised records. It does not automatically tell you whether somebody successfully accessed your account.
Check for signs of unauthorised activity.
These can include:
Login attempts from unusual locations
Security settings you did not change
Messages you did not send
Password reset notices you did not request
New connected devices
Unfamiliar recovery details
New email forwarding rules
Changes to bank beneficiaries
Orders you did not place
The NCSC advises breach victims to review their online accounts for suspicious activity and investigate when something appears unfamiliar.
If you believe an account has been compromised, follow the provider’s recovery process promptly.
Expect targeted phishing after a breach
Criminals can use breached information to make scams more convincing.
An attacker may already know your name, telephone number, employer or a service that you genuinely use.
A phishing email therefore does not always look random.
It may refer to a real account.
It may use your real name.
It may mention a genuine organisation.
It may even contain an old password.
None of these details proves that the sender currently controls your device or account.
The UK Government’s Cyber Security Breaches Survey 2025 to 2026 found that 43 per cent of businesses identified a cyber breach or attack during the previous 12 months. Phishing affected 38 per cent of businesses and remained the most commonly reported attack method.
This makes extra caution after a breach particularly important.
Do not trust an unexpected message simply because it knows something about you
Leaked data often gives criminals enough information to sound convincing.
They may know your:
Name
Email address
Telephone number
Employer
Previous address
Account history
Service provider
Old password
Treat unexpected contact independently from the information it contains.
If somebody claims to represent your bank, contact the bank through its official application or recognised contact route.
If an email claims that a cloud account needs urgent action, open the provider’s normal website rather than clicking the message.
If somebody claiming to be a supplier asks for payment details to change, verify the request through a separate trusted contact.
Accurate personal information makes a scam more believable, but it does not prove the sender’s identity.
Report suspicious emails and text messages
Reporting suspicious messages can help authorities and service providers disrupt scams.
The NCSC advises people to forward suspicious emails to report@phishing.gov.uk and suspicious text messages to 7726.
If you have lost money, contact your bank immediately.
The NCSC currently directs victims in England, Wales and Northern Ireland to Report Fraud. People in Scotland should contact Police Scotland.
Keep evidence where it may help.
Useful records can include:
Screenshots
Dates and times
Messages
Transaction references
Account alerts
Names used by the criminal
Details of telephone calls
Avoid continuing a conversation with the scammer simply to gather more evidence.
Protect yourself first.
Contact your bank when financial information may be involved
If a breach exposes bank or card information, contact the relevant provider through an official route.
Do not call a telephone number included in an unexpected warning message.
Review recent transactions and look for unfamiliar activity.
Check for:
Payments you do not recognise
New beneficiaries
Changes to contact details
Unfamiliar direct debits
Applications you did not make
The ICO advises people affected by data breaches to inform their bank, building society or card company about unusual transactions.
Continue monitoring accounts even if everything initially appears normal.
Criminals do not always use stolen information immediately.
Identity information needs a different response
A password can be changed.
Your date of birth cannot.
The same applies to your legal name, historical addresses and some identification information.
This makes identity-related exposure particularly important.
The ICO recommends that people who suspect identity theft act quickly. Its guidance advises victims to report lost or stolen identity documents, inform financial organisations of suspicious transactions and obtain a copy of their credit file to look for applications they do not recognise.
Watch for warning signs such as:
Unexpected credit applications
Financial accounts you did not open
Bills for unfamiliar services
Letters from debt collectors
Changes to your credit record
Missing post
Unexpected mobile accounts
Unfamiliar loan applications
If something does not look right, investigate promptly.
Identity fraud remains a major UK issue
Stolen personal information has real value to criminals.
Cifas reported more than 444,000 fraud-risk cases to its National Fraud Database during 2025, the highest annual total it had recorded. More than 242,000 involved identity fraud.
The problem has continued into 2026.
Cifas reported more than 220,000 fraud-risk cases during the first six months of 2026, with identity fraud accounting for 59 per cent of those records.
These figures help explain why exposed identity information deserves attention even when no immediate financial loss appears.
Criminals can hold information for later use or combine it with data obtained from another breach.
Consider additional identity protection where the risk is serious
The ICO points people towards Cifas Protective Registration when they face heightened identity fraud risk.
Protective Registration places an additional warning against a person’s details within the Cifas National Fraud Database so participating organisations can make additional checks when somebody applies for a financial service using those details.
This does not make identity fraud impossible.
It can provide an additional layer of verification when the risk justifies it.
Consider seeking specialist advice when sensitive identification records appear in a breach or you already see evidence of attempted impersonation.
Can I use a data breach checker UK?
Yes. UK individuals and businesses can use breach checking services to identify known exposure connected with an email address.
UK Cyber Security Group provides a free service specifically for this purpose. Its checker queries the email address against Have I Been Pwned and displays known breach results.
A checker should form part of a wider security approach.
Continue using unique passwords and stronger authentication even when the result is clean.
For businesses, breach checking can sit alongside:
Account management
Security awareness
Identity protection
Incident response
Security monitoring
Employee reporting processes
Domain monitoring
The value comes from responding to the result rather than simply running the search.
If your work email appears, tell your organisation
A breached business email address can create risks for both the employee and employer.
Tell your IT team, security team, manager or managed IT provider.
The organisation may need to:
Reset the account password
Revoke existing sessions
Review authentication
Check login history
Review administrator access
Examine email forwarding rules
Check related services
Monitor security alerts
Review other employee exposure
The NCSC advises people who interact with suspicious content on a work laptop or phone to tell their IT department.
Early reporting gives the organisation a better chance to detect misuse before it develops into a larger incident.
A business should assess whether it has suffered a personal data breach
An employee credential appearing in criminal data does not automatically mean that the business itself needs to report a personal data breach.
The organisation should investigate the facts.
The ICO advises businesses to assess which personal information was involved, who may suffer harm and how serious that harm could become.
Record what happened.
Contain unauthorised access.
Identify affected information.
Determine how many people may face risk.
Assess potential consequences.
Keep a record of the decisions.
Where a personal data breach is likely to create risk to people’s rights and freedoms, the organisation may need to notify the ICO. The ICO states that reportable incidents should reach it without undue delay and, where possible, within 72 hours of the organisation becoming aware of the breach.
When the risk to affected people is high, additional communication duties may also apply.
Do not assume that data can simply be removed from everywhere
People naturally want stolen information deleted from the dark web.
Unfortunately, once criminals copy information, nobody can guarantee deletion of every copy.
The data may have moved through several collections.
One criminal may have sold it to another.
Copies may exist offline.
The original source may no longer exist while redistributed copies remain.
Focus on making the exposed information less valuable.
Change the password.
Close an account you no longer need.
Enable stronger authentication.
Replace a compromised document where appropriate.
Watch financial accounts.
Monitor identity risk.
Tell your employer when business information appears.
This approach gives you practical control over the consequences even when you cannot control every copy of the stolen data.
Old breaches can still matter
Do not ignore a result simply because the breach happened years ago.
Ask whether the information still works.
An old password creates little direct account risk if you replaced it years ago and never reused it.
The same password becomes important when it still protects another service.
An old telephone number may matter less if you no longer control it.
A date of birth remains useful because it does not change.
A historic home address may still help criminals pass identity checks or construct convincing scams.
Judge the value of the exposed information rather than only the age of the incident.
Email addresses are more valuable than they look
An email address may seem harmless because people share email addresses routinely.
Criminals can still use one for several purposes.
They can send phishing messages.
They can try password reset processes.
They can search for related accounts.
They can combine it with another breach.
A company address may reveal the employer and help identify valuable employees such as directors, finance staff or administrators.
Protect the account even when the breach did not contain a password.
Review your recovery settings
Security does not stop with the password.
Review how important accounts recover access.
Check:
Recovery email addresses
Telephone numbers
Trusted devices
Backup authentication methods
Connected applications
Security questions
Remove anything outdated or unfamiliar.
An old recovery address that somebody else now controls can create a route around your new password.
Recovery arrangements deserve the same attention as the main login.
Close accounts you no longer use
Every forgotten online account creates another place where information can sit.
Review old services that you no longer need.
Where practical, close accounts and remove unnecessary personal information.
This will not remove historical breach information already copied by criminals.
It can reduce your future exposure by limiting the amount of personal information held by services you no longer use.
Businesses should apply the same thinking to employee and supplier accounts.
Inactive access should not remain available indefinitely.
Which companies provide dark web email checker in the UK?
UK Cyber Security Group provides a free email breach checker for individuals and organisations. The service checks the submitted email address against known breach information through Have I Been Pwned.
Other cyber security companies and identity monitoring providers also offer breach and dark web monitoring.
When comparing services, consider:
What information does the service search?
Does it explain the source?
Does it offer one-off checking or ongoing monitoring?
How does it handle the information you submit?
How quickly do alerts arrive?
Does it explain what you should do after a match?
Can it support business incidents involving employee credentials?
Avoid services that promise perfect visibility into all criminal networks.
No legitimate provider can guarantee knowledge of every private stolen-data collection.
Which UK-based firms offer data breach check services?
UK Cyber Security Group provides its free email breach checker together with broader cyber security services for businesses.
UK organisations can also obtain breach monitoring and response assistance from managed security providers, cyber security consultancies, identity protection organisations and threat intelligence specialists.
Choose the level of support according to your risk.
An individual may need one email search and straightforward account security advice.
A small business may want checks across employee accounts and a clear response process.
An organisation with many users may need ongoing domain monitoring, account security reviews and incident investigation.
Whatever service you use, somebody needs responsibility for acting on alerts.
Monitoring has little value when nobody reviews the findings.
Businesses should consider monitoring their company domain
A business email domain can appear across numerous external breaches without the organisation itself being hacked.
Employees may use work addresses to register with:
Software services
Training providers
Industry forums
Supplier portals
Professional associations
Events
Newsletters
If one of those services suffers a breach, the business address may enter stolen-data collections.
Ongoing monitoring can help the organisation identify new exposure earlier.
A sensible response process should identify who reviews alerts and what happens when a match appears.
The company can then check whether the exposed credential remains active and whether the affected account shows suspicious activity.
If you clicked a suspicious link, consider the device as well as the account
Sometimes a data warning follows a phishing incident rather than a known database breach.
If you opened a suspicious link but did not enter information or download anything, the NCSC says further action may not be necessary, although you should remain alert.
If you followed instructions that caused software to run or you downloaded something suspicious, the device may need attention.
The NCSC advises users in this situation to run their security software and allow it to address problems that it finds.
For a business device, report the event to IT rather than attempting to handle a potentially serious incident alone.
Keep records of what you have done
A simple record can become valuable when suspicious activity develops later.
Record:
Which breach you identified
When you identified it
What information appeared
Which passwords you changed
Which accounts you reviewed
Whether you contacted your bank
Whether you informed your employer
Any suspicious transactions
Any fraud reports
Any unusual login activity
Businesses should keep particularly good incident records.
The ICO advises organisations to record personal data breaches, including the facts, effects and remedial action, even when the incident does not require regulatory notification.
Good records help demonstrate that the organisation assessed the situation properly.
Keep checking after the immediate problem has been resolved
Changing an exposed password protects the account from continued use of that credential.
It does not erase all the information criminals already obtained.
Continue watching for:
Phishing
Account recovery attempts
Unexpected credit activity
Bank transactions
Unfamiliar logins
Impersonation
Suspicious calls
Criminals may wait before using compromised information.
Long-term vigilance matters particularly when permanent identity information has leaked.
Make future breaches less damaging
You cannot control every organisation that stores information about you.
You can control whether one organisation’s breach unlocks everything else.
Use a unique password for every important account.
Use a password manager when helpful.
Enable multi-factor authentication.
Use passkeys where appropriate.
Keep recovery information current.
Close accounts you no longer need.
Be cautious about how much personal information you share.
Keep business devices and applications current.
Teach employees how to recognise phishing.
Report suspicious activity quickly.
These habits reduce the potential impact of the next breach.
A practical order for responding
When a breach checker finds your information, work through the problem logically.
First, identify the service and the information involved.
Next, change any exposed password that remains active.
Change it anywhere else you reused it.
Secure your main email account.
Enable multi-factor authentication on important accounts.
Review account login activity and recovery settings.
Check financial accounts when financial information may have leaked.
Monitor identity information when permanent personal details appear.
Tell your employer when business credentials are involved.
Watch for phishing that uses real information about you.
Report suspicious communications.
Keep evidence of any genuine misuse.
Continue monitoring important accounts after the immediate changes.
This sequence helps turn an alarming notification into a manageable security response.
Use the free UK Cyber Security Group checker as an early warning
UK Cyber Security Group’s free email breach checker gives individuals and organisations a simple way to determine whether an email address appears in known breach information. The service queries Have I Been Pwned and recommends password changes and stronger authentication when a match appears.
A breach result should prompt action, not panic.
Determine what was exposed.
Make compromised credentials useless.
Protect your main accounts.
Monitor identity and financial activity where necessary.
Stay alert to scams that use genuine information to win your trust.
For businesses, take the extra step of investigating employee exposure and assessing whether any organisational systems or personal information have become compromised.
You may not be able to remove every copy of information that criminals have already obtained, but you can greatly reduce what they can do with it. Fast action, unique credentials, stronger authentication and ongoing awareness can turn a potentially serious exposure into a manageable security issue.
UK Cyber Security Group Ltd is here to help
Please check out our Free Cyber Insurance
Other blog posts, Your ISO 27001 Questions Answered, Get ISO 27001 Certified ,
If you would like to know more, do get in touch as we are happy to answer any questions. Looking to improve your cybersecurity but not sure where to start? Begin by getting certified in Cyber Essentials, the UK government’s scheme that covers all the technical controls that will provide the protection that you need to help guard against criminal attacks. Or just get in touch by clicking contact us


