
Why are my details are on the dark web?
Why are my details are on the dark web?
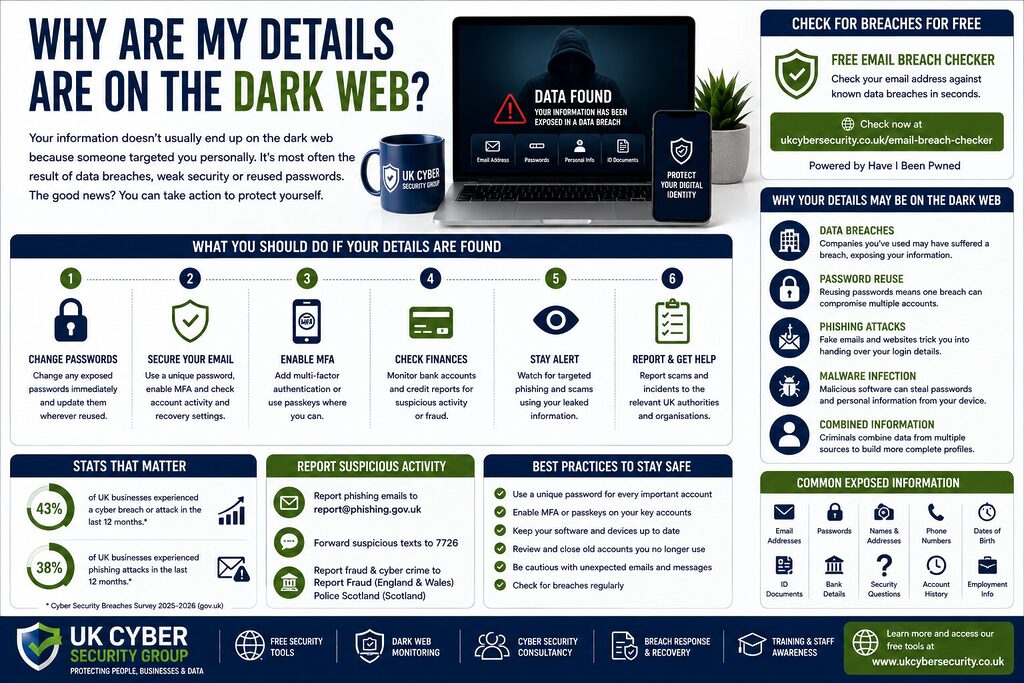
Finding your email address, password or personal information connected with the dark web can feel alarming. In most cases, however, your details did not reach criminal databases because somebody specifically targeted you. They often arrived there because an organisation you previously dealt with suffered a data breach, a password was stolen, malware captured information or criminals combined data from several older incidents.
The UK Cyber Security Group provides a free email breach checker that allows you to check an email address against known data breaches. Its checker queries Have I Been Pwned and can show whether an email address appears in known compromised records.
Understanding why your information has appeared is useful because the source of the exposure influences what you should do next. An exposed email address presents a different risk from an exposed password, identity document or financial record.
The important point is that information found in a breach should be treated as potentially available to criminals. You can then secure affected accounts, change reused passwords, strengthen authentication and watch for fraud or convincing phishing attempts.
Your information may have come from a company you trusted
One of the most common reasons personal information reaches criminal communities is a breach at an organisation that collected your details legitimately.
Think about how many organisations have held your information during the last decade:
Online retailers
Social networks
Employers
Utility companies
Mobile providers
Banks
Insurance providers
Travel companies
Healthcare providers
Forums
Subscription services
Cloud platforms
Professional organisations
Educational services
Recruitment businesses
Each organisation may hold an email address, name, telephone number, postal address, password record or other account information.
If attackers compromise one of those organisations, they may steal a large database containing information about thousands or millions of people.
Your presence in that dataset does not necessarily mean that criminals hacked your personal computer. You may simply have been one record in a much larger breach.
A significant UK example appeared in May 2026 when the Information Commissioner’s Office reported that personal information relating to 633,887 people had previously been published on the dark web following a cyber attack against South Staffordshire Plc and South Staffordshire Water Plc.
That example demonstrates an important point. Information can reach the dark web because an organisation holding customer or employee records suffers a security failure.
Old accounts can create current problems
People often forget how many websites they have joined.
You may have registered for a forum fifteen years ago, purchased something from a retailer you no longer use or created an account with a service that later disappeared.
The account may feel irrelevant today.
The information inside it may still matter.
Suppose you registered using:
Your main email address
A password you later reused
Your real name
Your date of birth
Your telephone number
Criminals who obtain that old database can combine those details with newer information.
An old breach can therefore create a current security problem.
The date of the breach matters less than whether the stolen information remains useful.
If you still use the same password somewhere else, change it.
If the exposed address remains your main email account, protect that account carefully.
Password reuse gives criminals another opportunity
Password reuse is one of the reasons a breach at one company can affect accounts held somewhere completely different.
Attackers take username and password combinations stolen from one service and try them against other services. The NCSC calls this credential stuffing.
Imagine that an old shopping website suffers a breach.
The criminals obtain:
ExamplePassword123
They may then test the same combination against email, social networks, online shopping, cloud storage or other services.
If Jane used a unique password on the breached shopping site, the damage may remain limited.
If she reused it across several accounts, one breach creates several opportunities.
The NCSC specifically advises against password reuse because passwords stolen from one service can be tried against another.
This explains why seeing an old password in a breach result should not be dismissed.
Ask whether you ever reused it.
If the answer is yes, replace it everywhere it remains active.
What is a data breach checker?
A data breach checker is a service that searches known compromised records for an identifier such as an email address.
UK Cyber Security Group provides a free checker that compares an email address with records available through Have I Been Pwned. It states that the service can identify whether an email address and related credentials have appeared in known breaches.
A checker does not need your current email password.
You should never submit an active password simply because a website claims that doing so will reveal whether it has leaked.
A reputable checker normally needs the identifier you want to search, such as an email address.
The result can identify known exposure and help you decide which accounts need attention.
It cannot prove that nobody possesses information about you elsewhere.
Some criminal databases remain private. Others may not yet have reached security researchers. New breaches may also take time to become known.
Think of a breach checker as an early warning system rather than a guarantee of complete visibility.
Criminals often combine information from several breaches
A single breach might contain little more than your email address.
Another may contain your telephone number.
A third could contain your old address and date of birth.
Criminals can combine those records.
The resulting profile may contain far more information than any single organisation lost.
This practice can help criminals create convincing impersonation attempts.
For example, a fraudulent email becomes more believable when the attacker knows:
Your full name
Your employer
An online service you genuinely use
Your telephone number
An old address
Part of your account history
None of these details necessarily proves that the attacker currently controls your account.
They may simply have combined leaked information from several sources.
That is why you should never trust unexpected contact purely because the sender knows accurate information about you.
Phishing can lead to stolen credentials
Not every compromised password comes directly from a breached database.
Some people enter their login information into fraudulent websites after receiving convincing phishing messages.
Attackers may impersonate:
Microsoft
A bank
A delivery company
An employer
A cloud provider
A social network
A customer
A supplier
They create a fake login page and persuade the victim to enter credentials.
Those credentials may then enter criminal databases or circulate among other attackers.
Phishing remains a major UK problem. The Cyber Security Breaches Survey 2025 to 2026 found that 38 per cent of UK businesses experienced phishing during the previous 12 months.
The same government research found that 43 per cent of businesses identified some form of cyber breach or attack during that period.
These figures show why exposed credentials should be treated seriously.
Malware can steal information from devices
Malicious software can also collect information directly from a computer.
Some malware focuses on credentials and information stored in browsers or applications.
This can potentially expose:
Saved passwords
Session information
Browser data
Account details
Email addresses
Cryptocurrency information
Business credentials
Attackers may package stolen information and distribute it to other criminals.
The presence of information in criminal records therefore does not always prove that the organisation named in a breach report lost it.
If you have reason to believe your own device suffered malware infection, changing passwords alone may not be enough. Make sure the device receives appropriate security review before using it to reset important credentials.
For a business device, involve your IT or cyber security team.
Company information can expose employees
Employees frequently discover company email addresses in breach records.
This does not automatically mean the employer’s own network suffered a breach.
A staff member may have registered their work address with an unrelated external service.
For example, someone might use a company email address for:
A professional forum
An industry newsletter
A software account
An event
A supplier portal
A training service
If that external provider suffers a breach, the work email address can enter criminal databases.
Attackers can then use the address to target the employee or organisation.
Business addresses have additional value because they often reveal:
The organisation’s domain
Employee names
Job roles
Email naming conventions
Departments
Potential targets
A criminal who identifies finance@company.co.uk or a Finance Director’s email address immediately gains useful targeting information.
How can get an email breach checker for free?
UK Cyber Security Group provides a free service that lets you check an email address against known breach records.
Its checker uses Have I Been Pwned as its underlying breach database. The UK Cyber Security Group page states that users can check whether an email address and associated credentials have appeared in known compromised information.
Using a reputable checker is much safer than attempting to search criminal websites yourself.
You do not need to enter hidden networks, join criminal forums or download leaked databases.
Enter the email address into the recognised checking service and review the result.
If a breach appears, identify:
The organisation involved
The date of the incident
The information reported as exposed
Whether the affected password remains active
Whether you reused that password elsewhere
Then secure the affected accounts.
What is the best free email breach check?
A useful free email breach check should have a reputable data source, explain what it searches and give clear advice when it finds a match.
UK Cyber Security Group provides a straightforward option for UK individuals and businesses because its checker searches Have I Been Pwned and provides guidance when an email address appears in known breached information.
Do not judge a service by dramatic claims.
No legitimate provider can promise that it sees every stolen record held by every criminal group.
Look for transparency.
A useful service should explain:
What you need to enter
What information it searches
What a positive result means
What a negative result means
What action you should take
How your submitted information receives protection
The purpose should be to help you reduce risk rather than frighten you.
Your information may have been shared repeatedly
Once information escapes into criminal communities, copies can spread.
One criminal may sell it.
Another may combine it with other records.
Someone else may republish the information.
The same email address may therefore appear in several collections.
This is why deleting information from one location does not guarantee that all copies disappear.
You usually have more control over the usefulness of the data than over every copy of it.
If an old password leaked, make it useless by changing it.
If an account has weak authentication, strengthen it.
If identity information leaked, increase fraud monitoring.
If a work credential appears, notify your employer.
Focus on reducing the value criminals can gain from the exposed information.
Public information can strengthen leaked information
Not every detail criminals know about you came from a breach.
Businesses and individuals publish significant amounts of information openly.
Company websites may list:
Employee names
Leadership teams
Job titles
Telephone numbers
Email addresses
Office locations
Supplier relationships
Social media adds further detail.
Criminals can combine this public information with breach records.
For example, a leaked email address combined with LinkedIn information may tell an attacker that the person works in finance.
That knowledge helps the criminal create a targeted payment scam.
Review what information your business makes public and ask whether every detail needs to be visible.
You do not need to hide legitimate company contact information.
You should understand how criminals may combine it with stolen data.
Identity information creates longer-term risk
An exposed password can be changed.
A date of birth cannot.
The same applies to a historical address, legal name or some identification information.
That makes identity-related breaches particularly important.
The ICO warns individuals to remain cautious about unexpected contact asking them to confirm personal information and advises people who experience a breach to watch for suspicious emails, texts and websites.
Identity fraud remains a substantial concern in the UK.
Cifas reported more than 242,000 identity fraud cases during 2025, accounting for 54 per cent of fraud-risk cases recorded to its National Fraud Database.
If sensitive identity information appears in a breach, monitor your financial and identity records carefully.
Can I use a data breach checker UK?
Yes. UK individuals and businesses can use a breach checker to identify known exposure linked to an email address.
UK Cyber Security Group provides a free email breach checker for this purpose.
The service can provide a useful starting point for UK users who want to understand whether an address has appeared in known compromised information.
A checker should form part of wider security.
Continue to use:
Unique passwords
Multi-factor authentication
Secure devices
Current software
Careful account recovery settings
Fraud monitoring
Staff awareness
A clean result today does not guarantee that a breach will not appear tomorrow.
New information can emerge later.
Why an email address is valuable to criminals
People sometimes assume that an email address has little value because it appears publicly in many places.
Context makes the difference.
Your email address can act as the username for dozens of accounts.
It may also reveal your employer or identity.
Criminals can use it for:
Credential stuffing
Phishing
Impersonation
Password reset attempts
Account discovery
Targeted scams
Business email fraud
A leaked email address combined with a leaked password becomes significantly more dangerous.
The NCSC recommends additional authentication because passwords can be stolen through several routes and attackers continually attempt to reuse compromised credentials.
Protect your main email account carefully
Your main email account deserves strong protection because it often controls password resets for other services.
Use a unique password.
Enable multi-factor authentication.
Consider a passkey where your provider supports it.
Review active sessions.
Check recovery details.
Look for unfamiliar forwarding rules.
Remove connected applications you no longer use.
Investigate unexpected login notifications.
If you suspect compromise, secure the email account before resetting passwords for less important services.
An attacker who still controls your email could otherwise reset the new credentials again.
A positive result does not always mean your current password leaked
Read the breach result carefully.
A service may report that your email address appeared in a breach without saying that your password appeared.
Another incident may include:
Names
Telephone numbers
Addresses
Dates of birth
Account history
Password hashes
Security questions
The risk depends on what the attackers obtained.
Do not assume the worst, but do not ignore the result.
Identify the exposed information and respond according to the actual risk.
A clean result does not guarantee complete safety
People sometimes misunderstand a negative breach-check result.
It does not prove that nobody has your information.
It means the checker did not identify the address within the records it searched.
There may be:
A recent undisclosed breach
A private criminal dataset
A phishing incident
Malware on a device
A compromised account that has not appeared in a known database
Information collected from public sources
Continue using good security even when the result is clear.
Which companies provide dark web email checker in the UK?
UK Cyber Security Group provides a free email breach checker that queries Have I Been Pwned for known breach information.
The company also provides dark web monitoring aimed at businesses that want ongoing visibility of leaked email addresses and passwords.
Other cyber security providers and identity monitoring companies also offer breach monitoring services.
When choosing one, look for a provider that clearly explains its sources and limitations.
Ask whether the service provides:
A one-off search
Ongoing monitoring
Company domain monitoring
Credential alerts
Clear remediation guidance
Business support after a match
Avoid exaggerated claims about complete visibility across criminal networks.
Which UK-based firms offer data breach check services?
UK Cyber Security Group offers a free individual email breach checker alongside broader dark web monitoring services for businesses.
Other UK cyber security consultancies, managed security companies and identity protection providers may also provide breach detection and monitoring.
The right service depends on what you need.
An individual may only want to know whether one email address appears in known breach records.
A business may need monitoring across an entire company domain.
Larger organisations may want the findings connected with incident response, security monitoring, user awareness and account management.
The key requirement is action.
Finding exposed information only creates value when somebody reviews the result and reduces the associated risk.
Why businesses should monitor exposed employee accounts
For businesses, leaked credentials can provide an attacker with a starting point.
Even when the old password no longer works, the criminal may learn useful information about the employee and organisation.
Monitoring can help identify exposure affecting:
Senior management
Finance teams
IT administrators
Sales teams
Shared mailboxes
Customer service
Remote access accounts
Supplier contacts
Employees should have a simple route for reporting breach notifications.
The security or IT team can then determine whether the credential remains active and whether further investigation is necessary.
What should I do when my details appear?
Start with the affected account.
Change any exposed password that still works.
Replace the credential anywhere else you reused it.
Protect your email account with multi-factor authentication.
Check account sessions and login history.
Review recovery information.
Watch for phishing that refers to the breached service.
If financial information appears, contact your bank through a trusted route.
If identity information appears, review credit records and monitor for applications you do not recognise.
If work credentials appear, notify your organisation.
The ICO advises people affected by a breach to watch for suspicious communication, inform financial providers of unusual transactions and report compromised official documents to the organisation that issued them.
Do not panic because someone knows an old password
Scammers sometimes send threatening messages containing a password you previously used.
They may claim that they hacked your computer or possess damaging information.
The old password may simply have come from a historic breach.
Its presence proves that the criminal knows that credential.
It does not automatically prove every other claim in the message.
Do not pay money or follow instructions solely because someone includes a real old password.
Change the credential wherever it remains active and report suspicious communications.
Why dark web exposure matters even years later
Criminal data can remain useful for a long time.
Old information helps attackers:
Build profiles
Identify accounts
Create believable phishing
Answer identity questions
Target businesses
Connect different online identities
This explains why an incident from years ago can still matter today.
A breach checker gives you visibility into known historic exposure so you can reduce its value.
Make future breaches less damaging
You cannot stop every organisation you deal with from suffering a cyber attack.
You can reduce the effect when one does.
Use a different password for each important account.
Enable multi-factor authentication.
Use passkeys where appropriate.
Avoid sharing unnecessary personal information.
Keep devices and software current.
Monitor important financial accounts.
Review old accounts and close those you no longer need.
Train staff to recognise phishing.
Maintain good user access management within your business.
A future breach becomes much less useful to criminals when the stolen password works nowhere else.
Why checking regularly makes sense
New breach information appears over time.
An email address that produces no results today may appear later when researchers obtain data from an older incident or a new organisation announces a breach.
Periodic checking provides another opportunity to detect that exposure.
Businesses can consider ongoing monitoring when several employee accounts, customer services or critical identities need protection.
UK Cyber Security Group’s monitoring service is designed to identify when company email addresses or passwords appear in dark web information.
Your details are usually there because data travels
Personal information moves through many organisations during ordinary life.
You give your details to employers, online services, retailers, financial providers, professional organisations and cloud platforms.
Every copy creates another place where security matters.
Sometimes an organisation suffers a breach.
Sometimes a user falls for phishing.
Sometimes criminals steal credentials through malware.
Sometimes old databases circulate for years.
This is why finding your information connected with the dark web does not automatically mean somebody deliberately selected you as a target.
It does mean that you should treat the exposed information carefully.
Use UK Cyber Security Group’s free email breach checker to identify known exposure linked to your email address.
Then focus on what matters most: replace compromised passwords, strengthen authentication, protect your main email account, monitor identity and financial information, and stay alert for phishing that uses genuine information to gain your trust.
Once information has escaped, you may not be able to control every copy. You can make that information far less useful to criminals by securing the accounts and services it could otherwise help them attack.
UK Cyber Security Group Ltd is here to help
Please check out our Free Cyber Insurance
Other blog posts, Your ISO 27001 Questions Answered, Get ISO 27001 Certified ,
If you would like to know more, do get in touch as we are happy to answer any questions. Looking to improve your cybersecurity but not sure where to start? Begin by getting certified in Cyber Essentials, the UK government’s scheme that covers all the technical controls that will provide the protection that you need to help guard against criminal attacks. Or just get in touch by clicking contact us


